TLP:CLEAR · Disclosure is not limited.
Europe Hybrid Threats: Attribution Remains Uneven
Time window: Last 1 day · Audience: General analyst · Type: Situation report · DTG: 2026-11-19 17:40Z · Overall confidence: HIGH
BLUF
Reporting describes Russian-linked information activity and several suspected sabotage incidents affecting support for Ukraine, but the material does not establish a coordinated Russian-directed campaign across Europe. The strongest incident-level allegations rely on thin, single-source reporting, so analysts should separate the reported events from attribution and intent.
Executive summary
The current reporting adds allegations of Russian-linked influence activity in Poland, Germany, the UK and around Ceuta, alongside reports of damage to weapons factories in Italy and Bulgaria and a foiled drone attack at Leipzig airport. Attribution varies: some accounts explicitly allege Russian involvement, while others identify no perpetrator. Most of these claims come from think-tank reporting without independent corroboration in the material provided. This brief does not establish a new, verified pattern of Russian-directed sabotage in Europe.
Change from previous assessment
Since the 18 November brief, the reporting adds allegations of influence activity in Poland, Germany, the UK and around Ceuta, as well as claims about incidents in Italy, Bulgaria and Leipzig. This broadens the geographic picture but does not independently corroborate Russian direction of the reported sabotage incidents or materially raise confidence in the threat assessment. The prior brief's separate reporting on Poland's border measures and Finland's border security law is not updated in the material for this run.
Key judgments
- Russian-linked information activity is likely intended to weaken support for Ukraine in Poland and Germany, but confidence in its current scale and operational direction is low. A think-tank analysis reports coordinated anti-Ukrainian economic narratives in Poland, says Russian Special Services expect to obstruct EU funding for Ukraine, and attributes subversion aimed at fracturing support for Ukraine to Russia in Germany and Poland. These allegations rest on think-tank reporting and lack independently corroborated technical evidence in the material provided. (Confidence: low · ASSESSED)
- I&W: Confirmation: Polish or German authorities or platform transparency reports publish technical findings that identify coordinated accounts amplifying anti-Ukrainian narratives around EU funding for Ukraine. (0-3 months)
- I&W: Break: an independent review finds the cited Polish narratives were not coordinated or linked to Russian direction. (0-6 months)
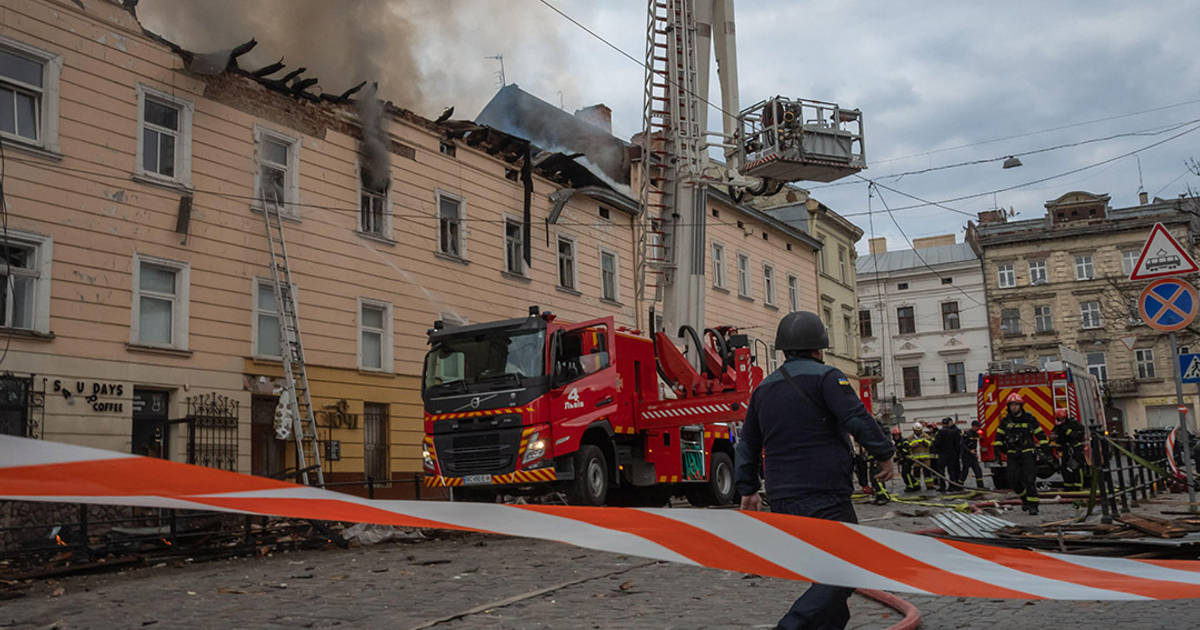
- It is unlikely that the current reporting establishes a Russia-directed sabotage campaign in Europe. A think-tank account reports an explosion damaging an Italian weapons factory that supplied munitions to Ukraine, a fire at a similar factory in Bulgaria, and a foiled drone attack on a Ukraine resupply aircraft at Leipzig airport. The claims name no perpetrators and provide no incident dates, leaving the incidents' relationship and attribution unresolved. (Confidence: low · ASSESSED)
- I&W: Confirmation: police, prosecutors or facility operators publicly link one or more of the Italian, Bulgarian or Leipzig incidents to common methods or Russian tasking. (0-6 months)
- I&W: Break: official investigative findings attribute the incidents to unrelated causes or perpetrators with no Russian connection. (0-6 months)
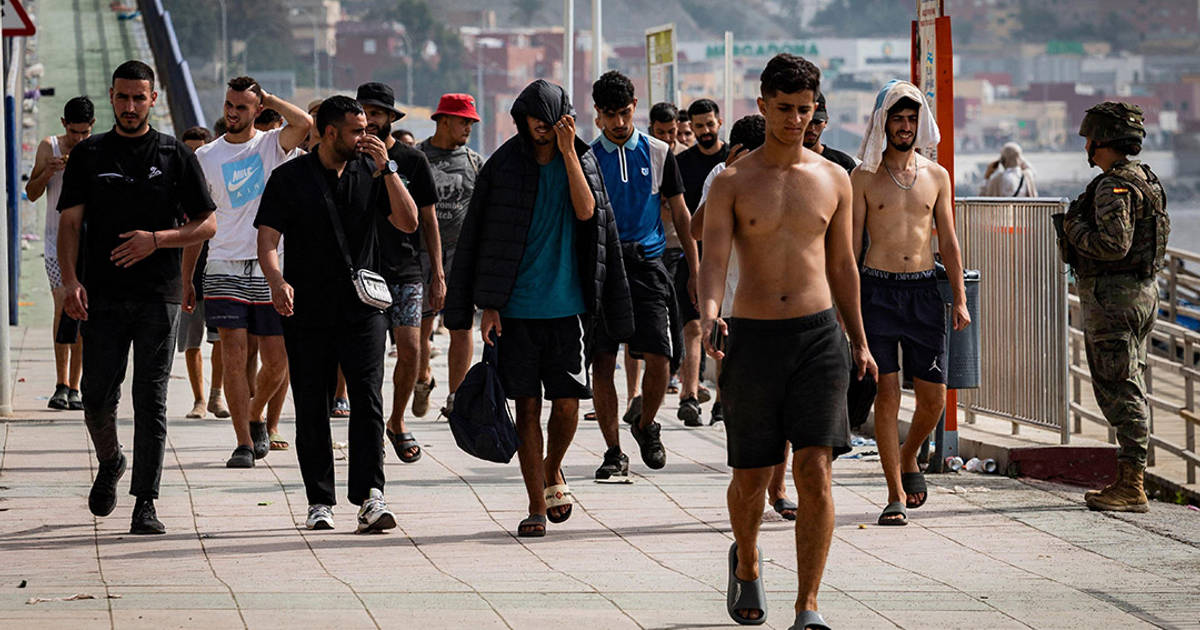
- Reports indicate that disinformation has been used to exploit migration and intercommunal tensions in Europe, but Russian attribution is uneven. A think-tank account attributes disinformation that encouraged more than 70,000 young Moroccans to storm Ceuta beach to Russia's hybrid warfare, and reports a Russian campaign amplifying an arson attack on the then British Prime Minister's private residence. The same account says pigs' heads were placed outside nine Paris mosques to inflame tensions, but names no perpetrator. The claims are not independently corroborated in the material provided. (Confidence: low · REPORTED)
- I&W: Confirmation: public platform or government analysis identifies Russian-linked networks amplifying content about Ceuta, the UK arson attack or the Paris mosque incidents. (0-6 months)
- I&W: Break: investigative findings show the cited incidents or related online activity were not coordinated or were unrelated to Russian actors. (0-6 months)
Outlook & scenarios
Persistent influence activity, limited verified physical attribution (60%)
Over the next 1-3 months, Russian-linked narratives are likely to continue exploiting existing disagreements over Ukraine, migration and social cohesion. European authorities are unlikely to establish a common Russian direction for the reported factory and Leipzig incidents without new investigative findings.
Public attribution prompts closer European coordination (25%)
A public investigation is likely to connect one or more reported incidents to a common actor or method. If authorities identify Russian direction, Poland, Germany, Italy and Bulgaria are likely to face pressure to coordinate investigations and share threat information.
Low-probability, high-impact attack triggers a political crisis (10%)
A further sub-threshold operation is unlikely to cause mass casualties, but an attack that does so would have high impact. It would likely intensify public scrutiny of European security measures and disputes over attribution, particularly if early reporting conflicts.
Recommendations
- Maintain a case-by-case incident ledger for the Italian and Bulgarian weapons factories and the Leipzig airport incident. Record the incident date, confirmed damage, investigative status, identified perpetrators and source basis separately.
- Track anti-Ukrainian narratives in Poland and Germany alongside EU funding decisions. Require platform data, official findings or independent technical analysis before treating narrative coordination as evidence of Russian tasking.
- Compare Poland's reported social-media monitoring, journalist and NGO training, and fact-checking infrastructure with Sweden's Psychological Defence Agency model when assessing national resilience options.
- In briefings, distinguish confirmed event details from claims about Russian direction or intent. Present alternative explanations when investigators have not publicly identified a perpetrator.
Confidence & uncertainty
The overall high rating reflects the corroboration scoring of the full event set and its mix of official, major-media, wire-service and think-tank reporting. It does not transfer automatically to the hybrid-threat judgments in this brief: the specific European sabotage and influence allegations rely heavily on think-tank accounts, and their attribution and operational links remain uncertain.
Alternative analysis (red cell)
The available material may support a narrower assessment that anti-Ukrainian and migration-related narratives circulated in Europe, but it does not establish that Russian actors currently directed or coordinated the activity. The cited claims are B1 and lack technical, forensic, or independently corroborated attribution, so Russian intent should remain unconfirmed rather than assessed as likely.
Intelligence gaps
- [EEI 1.2 · UNCOVERED] Observed reconnaissance activity around critical sites indicative of attack planning (unauthorised drone flights, repeated surveillance visits, loitering vehicles, mapping/photography of assets). Recommended collection: open-source/media
- [EEI 1.3 · UNCOVERED] Law-enforcement or customs seizures, arrests or interdictions of persons or shipments carrying explosives, sabotage tools, specialty cutting/electrical equipment, or covert comms gear destined for/near critical infrastructure. Recommended collection: law enforcement
- [EEI 2.1 · PARTIAL] Emergence or amplification of coordinated social-media networks (sets of accounts, pages, channels) pushing identical narratives or hashtags across multiple platforms, including bot-like activity metrics and origin IP/common management indicators. Recommended collection: social-media/OSINT
- [EEI 2.2 · PARTIAL] Publication or internal guidance from state-run media, proxy outlets, or identified influence platforms distributing talking points, pre-scripted messaging, or translated content targeted at specific EU countries/communities. Recommended collection: open-source/media
- [EEI 2.3 · PARTIAL] Distribution of manipulated multimedia (deepfakes), targeted phishing/whaling campaigns, or localized false narratives timed to political events (elections, protests, court rulings) with tracked reach and engagement metrics. Recommended collection: cyber/forensic
- [EEI 3.1 · UNCOVERED] Unusual financial transactions: wire transfers, crypto conversions, or payments to shell companies, NGOs or individuals exceeding typical baselines that link to known proxies or front organisations. Recommended collection: financial
- [EEI 3.2 · PARTIAL] Travel and movement indicators for suspected operatives: repeated border crossings, chartered/irregular flights, booking patterns or mobile/location data placing identified individuals in staging areas shortly before incidents. Recommended collection: border/immigration
- [EEI 3.3 · UNCOVERED] Cargo, freight or maritime movements with discrepancies (concealed/dual-use equipment, false manifests, unusual routing) detected at ports, rail hubs or via AIS that correspond to deliveries of material used in sabotage or influence operations. Recommended collection: customs/ports
- [EEI 3.4 · PARTIAL] Intercepted or otherwise-obtained communications showing tasking, coordination, or payment instructions between Russian agencies/handlers and proxy groups, including identified command-and-control servers or encrypted group identifiers. Recommended collection: signals-intel/SIGINT
Red cell review: PARTIAL DISSENT
TLP:CLEAR