TLP:CLEAR · Disclosure is not limited.
Europe Hybrid Threats: New Attributions, Persistent Evidence Gaps
Time window: Last 1 day · Audience: General analyst · Type: Situation report · DTG: 2026-10-15 13:09Z · Overall confidence: HIGH
BLUF
Poland and Estonia have publicly attributed separate arson attacks to Russia, adding case-specific claims absent from the previous brief. The reporting does not provide public evidence of Russian tasking, and other incidents are linked to a distinct Iran-related threat picture.
Executive summary
Reporting on 15 October adds two named cases to the European hybrid-threat picture: an arson attack on a Starlink ground station in Wola Krobowska, Poland, and an attack on Milrem Robotics in Tallinn, Estonia. Authorities in both countries attributed the incidents to Russia, but the available claims do not detail evidence establishing Russian direction. UK Prime Minister Andy Burnham attributed a suspected plot at RAF Fairford to Iran, while Dutch authorities are investigating Iranian links to a synagogue attack in Rotterdam. At EU level, the European Security Council remains a proposal, with no agreed legal basis, budget or launch date.
Change from previous assessment
This brief adds two specific attacks that Poland and Estonia have publicly attributed to Russia: the Milrem Robotics arson in Tallinn on 15 August and the Starlink ground-station arson in Wola Krobowska on 23 September. The prior brief said public reporting did not link specific recent European incidents to Russian tasking. The new cases raise the salience of Russia-linked sabotage, but do not establish Russian direction; confidence in case-level attribution remains limited. This brief also separates the reported Iran-related cases from the Russia-attributed incidents and notes that the European Security Council remains a proposal.
Key judgments
- It is likely that Russia-linked sabotage will remain a live European security risk over the next three months, but public reporting does not establish Russian tasking in the attacks on Milrem Robotics in Tallinn on 15 August or the Starlink ground station in Wola Krobowska on 23 September. Estonian authorities and Poland have attributed the attacks to Russia; the supplied reporting does not present case-level evidence supporting those attributions, so confidence is medium. (Confidence: medium · ASSESSED)
- I&W: Polish or Estonian authorities publicly identify suspects or release evidence linking either attack to Russian handlers. (0-3 months)
- I&W: Polish or Estonian authorities revise their Russian attribution, or publicly identify a non-Russian motive for either attack. (1-3 months)
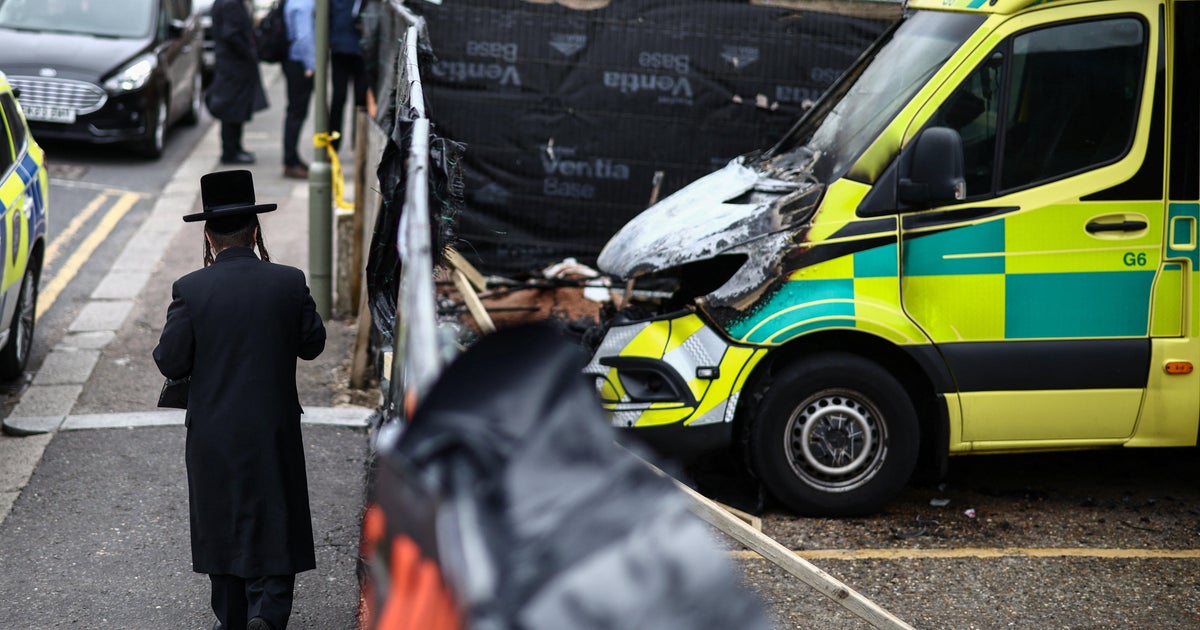
- It is unlikely that the available reporting supports treating all listed European sabotage incidents as one Russia-directed campaign. Andy Burnham said the suspected RAF Fairford plot was almost certainly directed by Iran; Dutch authorities are investigating Iranian links to the 13 March synagogue firebombing in Rotterdam. These attributions and investigations come from a reporting summary rather than public case evidence, so confidence is medium. (Confidence: medium · ASSESSED)
- I&W: UK authorities publish charging documents or investigative findings identifying Iranian direction in the RAF Fairford case. (0-3 months)
- I&W: Dutch authorities publicly rule out Iranian links to the Rotterdam synagogue attack. (1-3 months)
- The European Security Council is unlikely to provide an operational response to hybrid threats in the next three months. The European Commission has outlined a proposed structure and the European Parliament has called for a more proactive approach, but no formal legislative proposal, legal basis, budget or launch date has been agreed; confidence is medium because the proposal’s status is clear while its prospects are not. (Confidence: medium · ASSESSED)
- I&W: The European Commission tables a formal proposal naming a legal basis, budget and implementation timetable. (0-3 months)
- I&W: No formal proposal or implementation timetable is published by the end of the next three months. (1-3 months)
Outlook & scenarios
Isolated incidents, contested attribution (60%)
The most likely scenario is that reported sabotage remains a series of separate cases. Poland and Estonia maintain their Russia attributions, but public evidence does not establish a shared direction mechanism. The European Security Council remains under discussion while existing EU measures continue.
Investigations strengthen attribution and coordination (25%)
Investigative disclosures in Poland or Estonia provide case-level evidence linking suspects to Russian handlers. EU institutions advance the European Security Council proposal into a formal process, with defined responsibilities and resources.
Mixed attribution complicates response (10%)
Public findings reinforce the distinction between Russia-attributed attacks in Poland and Estonia and Iran-linked cases in the UK or Netherlands. Different national assessments complicate a common European response, while the proposed EU mechanism remains unimplemented.
High-impact wildcard: another attack with disputed attribution (5%)
A further arson or sabotage incident at a European satellite ground station or defence supplier causes casualties. Conflicting public attributions generate immediate political pressure for a response before investigators establish responsibility.
Recommendations
- Maintain separate incident records for the Wola Krobowska ground-station arson, the Milrem Robotics attack and the RAF Fairford plot. Record the incident itself, each authority’s attribution and any publicly disclosed evidence as distinct items.
- Prioritise updates from Polish and Estonian investigators that identify suspects, charges, communications or other evidence linking the attacks to Russian direction.
- Track UK findings on RAF Fairford and Dutch findings on the Rotterdam synagogue attack separately from Russia-attributed cases; do not combine them into a single campaign without evidence of coordination.
- Monitor for a formal European Commission proposal on the European Security Council, including its legal basis, budget, membership and implementation timetable. Until then, assess it as a policy proposal rather than an operational capability.
Confidence & uncertainty
Overall confidence is high in the broad situation because the main incidents and policy developments are reported by established media, with several attributions or statements tied to named government officials. Confidence is lower on Russian direction in the Poland and Estonia cases: the supplied reporting records official attributions but does not present case-level evidence. The RAF Fairford and Rotterdam reporting also reflects a separate Iran-related line of inquiry.
Intelligence gaps
- [EEI 1.2 · UNCOVERED] Observed reconnaissance activity around critical sites indicative of attack planning (unauthorised drone flights, repeated surveillance visits, loitering vehicles, mapping/photography of assets). Recommended collection: open-source/media
- [EEI 1.3 · UNCOVERED] Law-enforcement or customs seizures, arrests or interdictions of persons or shipments carrying explosives, sabotage tools, specialty cutting/electrical equipment, or covert comms gear destined for/near critical infrastructure. Recommended collection: law enforcement
- [EEI 2.1 · UNCOVERED] Emergence or amplification of coordinated social-media networks (sets of accounts, pages, channels) pushing identical narratives or hashtags across multiple platforms, including bot-like activity metrics and origin IP/common management indicators. Recommended collection: social-media/OSINT
- [EEI 2.2 · UNCOVERED] Publication or internal guidance from state-run media, proxy outlets, or identified influence platforms distributing talking points, pre-scripted messaging, or translated content targeted at specific EU countries/communities. Recommended collection: open-source/media
- [EEI 2.3 · UNCOVERED] Distribution of manipulated multimedia (deepfakes), targeted phishing/whaling campaigns, or localized false narratives timed to political events (elections, protests, court rulings) with tracked reach and engagement metrics. Recommended collection: cyber/forensic
- [EEI 3.1 · UNCOVERED] Unusual financial transactions: wire transfers, crypto conversions, or payments to shell companies, NGOs or individuals exceeding typical baselines that link to known proxies or front organisations. Recommended collection: financial
- [EEI 3.2 · UNCOVERED] Travel and movement indicators for suspected operatives: repeated border crossings, chartered/irregular flights, booking patterns or mobile/location data placing identified individuals in staging areas shortly before incidents. Recommended collection: border/immigration
- [EEI 3.3 · UNCOVERED] Cargo, freight or maritime movements with discrepancies (concealed/dual-use equipment, false manifests, unusual routing) detected at ports, rail hubs or via AIS that correspond to deliveries of material used in sabotage or influence operations. Recommended collection: customs/ports
- [EEI 3.4 · UNCOVERED] Intercepted or otherwise-obtained communications showing tasking, coordination, or payment instructions between Russian agencies/handlers and proxy groups, including identified command-and-control servers or encrypted group identifiers. Recommended collection: signals-intel/SIGINT
Cited sources
[1] CBS News · Iran and Russia-linked hybrid attacks in Europe are mounting, U.K. spy chief says. Here's a look at recent incidents. (A) · 14 October 2026 · sha256:e66872455010 [2] Euronews (Russian edition) · Европейский совбез поможет в борьбе с гибридными атаками России? (B) · 15 October 2026 · sha256:f77b8632aed2 [3] Euronews · Can a European Security Council help the EU fight Russia’s hybrid war? (B) · 15 October 2026 · sha256:57c52c55e9ba
Source content hashes were computed at collection time; the cited text is preserved unmodified for the life of this product.
Red cell review: CONCUR WITH COMMENT
TLP:CLEAR