TLP:CLEAR · Disclosure is not limited.
Europe Hybrid Threats: New Black Sea Strikes and Estonia Plot
Time window: Last 1 day · Audience: General analyst · Type: Situation report · DTG: 2026-11-16 13:36Z · Overall confidence: MEDIUM
BLUF
New drone strikes near Romania’s Sulina Canal and Norway’s warning about Russian-linked sabotage add to the reported threat picture, but public reporting does not establish responsibility for the Black Sea attacks or independently substantiate the GRU attribution in Estonia. Estonia’s planned border closure and EU action against a suspected Russian shadow fleet tanker show a response taking shape, though the effects remain untested.
Executive summary
Estonian authorities say they foiled an attempted explosion and arson at drone manufacturer Threod Systems in Viimsi on 14 November and detained eight suspects, all residents of Latvia. Estonia attributes the attempt to Russia’s GRU; Dmitry Peskov rejects the accusation, and the reporting available here gives no underlying case evidence. Romanian officials report three vessels hit by drones near Sulina over the weekend of 14-15 November, with two strikes inside Romanian territorial waters and no reported casualties. A separate report places the general cargo ship Larissa 1 in the same area on 13 November, leaving the incident count unclear. Romania has not identified the drones’ origin. Norway’s PST warns of Russian-linked sabotage and reports reconnaissance of infrastructure, while saying it has detected no physical sabotage in Norway to date. Separately, Romania’s SRI attributes a December 2025 cyberattack on a government body to Turla, an attribution Russia denies. Estonia plans to close its border crossings with Russia from 1 December; EU Operation Irini has also boarded the tanker MV Midag, which it said was sailing under a false flag.
Change from previous assessment
Since the 15 November brief, the assessment adds the reported Sulina strikes inside Romanian territorial waters, a separate report of the Larissa 1 strike, Norway’s PST warning and reconnaissance reporting, and SRI’s Turla attribution for a December 2025 cyberattack. These developments broaden the reported threat picture but do not resolve attribution. The Threod Systems incident and Estonia’s planned 1 December border closure remain part of the assessment; new reporting still does not independently establish the GRU link or confirm implementation of the closure. No new evidence in this reporting window changes the prior assessments of the November hoax threats or Germany’s intelligence reform.
Key judgments
- It is likely Estonian authorities foiled an attempted explosion and arson at Threod Systems in Viimsi at about 03:00 on 14 November. Eight suspects, all residents of Latvia, were detained. Estonia’s KAPO attributes the attempt to the GRU, while Dmitry Peskov rejects the accusation; the reporting available here does not describe evidence establishing Russian tasking. (Confidence: medium · REPORTED)
- I&W: Estonian court filings or a KAPO statement identify communications, payments or tasking links to GRU officers. (0-3 months)
- I&W: Estonian prosecutors withdraw or materially narrow the GRU attribution in public court filings. (0-3 months)
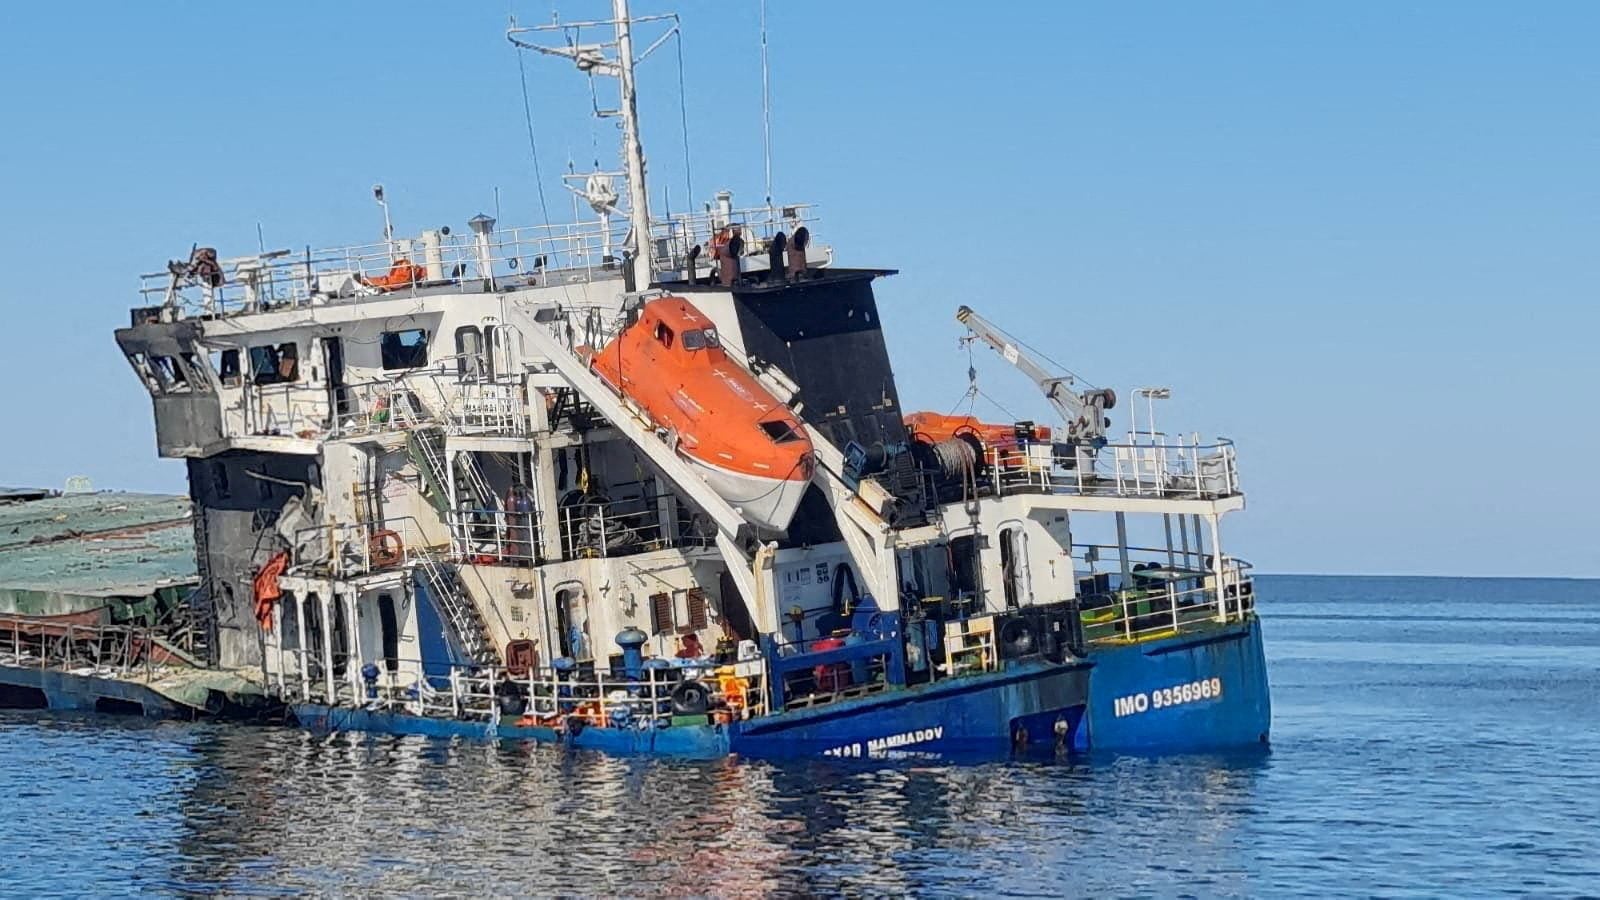
- It is likely that the Sulina strikes will continue to impose maritime and air-defence demands on Romania in the near term, but public reporting does not establish who launched the drones. Romanian reporting says three vessels were hit over the weekend of 14-15 November; Romania’s Defence Ministry placed Evia Petrol V and Marsol 4 and 5 nautical miles southeast of Sulina, inside Romanian territorial waters. Defence Minister Stefan Radu Oprea named Ali Najafov as the third vessel and reported no casualties. Separately, Larissa 1 was reportedly hit on 13 November, and the reporting does not resolve whether it was an additional vessel in the same sequence. (Confidence: medium · ASSESSED)
- I&W: Romanian authorities issue a new navigation warning or scramble aircraft in response to a drone alert off Sulina. (0-14 days)
- I&W: Romanian authorities report no further drone alerts, airspace incursions or ship strikes off Sulina for 30 consecutive days. (0-30 days)
- Norway’s PST warns of Russian-linked sabotage threats over the next 12 months and reports reconnaissance of infrastructure and potential targets by people linked to Russian intelligence. The service says it has detected no physical sabotage in Norway so far. This judgment is low confidence because the detailed account available here comes from one trade-publication report; Russia’s Embassy in Oslo rejects the allegations. (Confidence: low · REPORTED)
- I&W: Norwegian authorities announce an arrest or disrupted arson, explosives or drone plot involving a defence plant, military supplier, logistics firm or energy installation. (0-3 months)
- I&W: PST’s next public threat update withdraws its Russian-linked reconnaissance finding or downgrades the sabotage warning. (3-12 months)
- It is unlikely that the public record establishes Russian state responsibility for the December 2025 cyberattack on a Romanian government body. Romania’s SRI attributes the attack to Turla and says it coordinated with EU and NATO partners, but the reporting does not provide forensic evidence; Russia’s Embassy in Bucharest calls the allegation fabricated. (Confidence: medium · ASSESSED)
- I&W: SRI or its EU and NATO partners publish technical indicators or forensic findings linking the intrusion to Turla. (1-3 months)
- I&W: An independent forensic assessment attributes the intrusion to another actor or states that Turla attribution cannot be verified. (1-3 months)
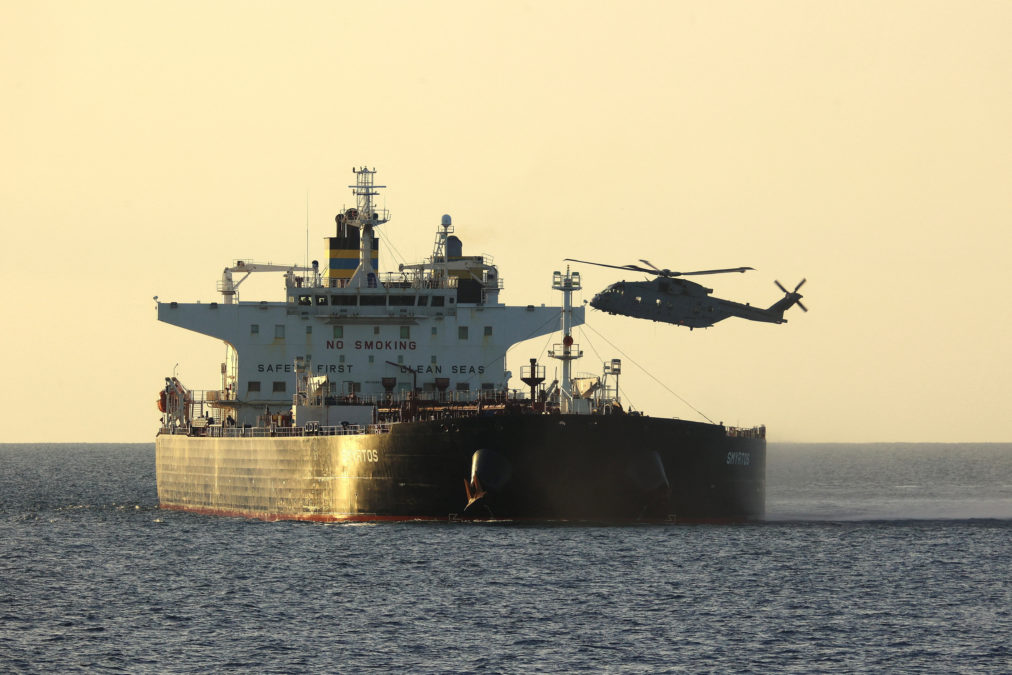
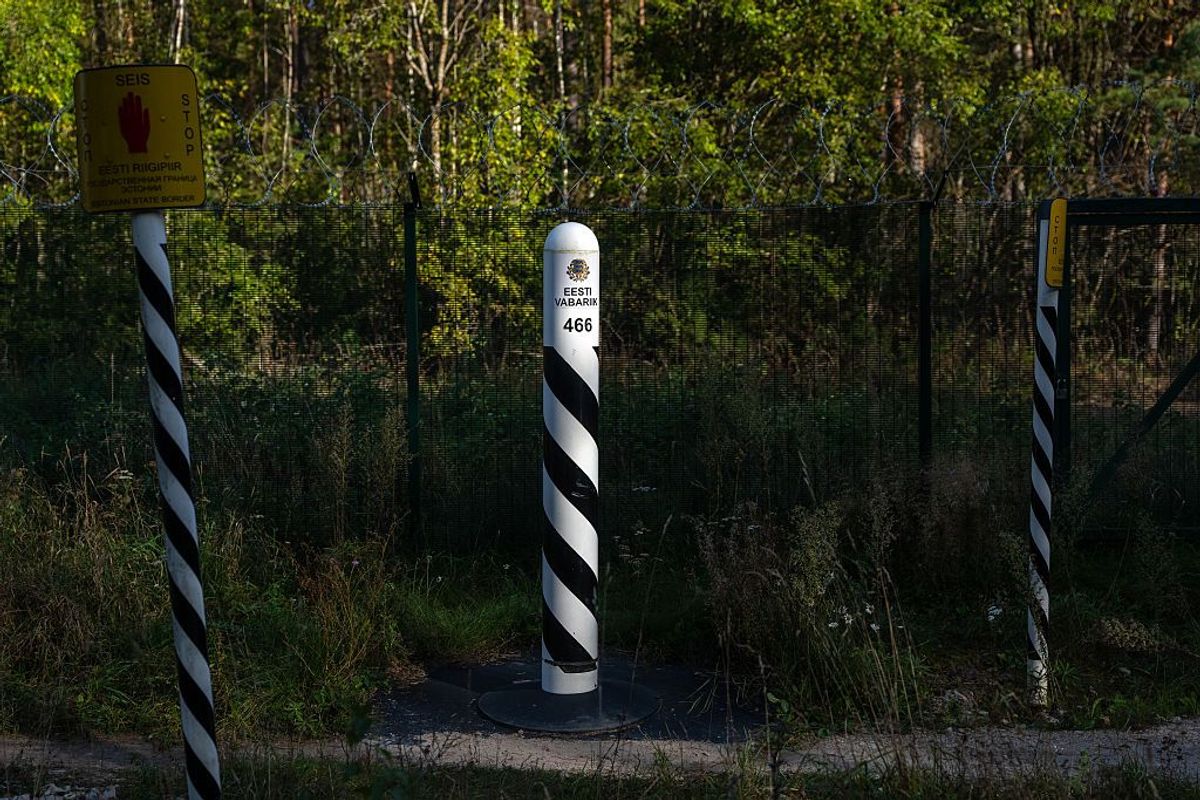
- European countermeasures now include a planned Estonian border closure and maritime enforcement against suspected Russian shadow fleet activity, but their effects remain untested. Estonia announced that all border crossings with Russia will close from 1 December. Operation Irini boarded MV Midag on 13 November and reported that the tanker was sailing under a false flag. France has announced a Paris conference on the shadow fleet for 4 December; EU sanctions listings targeting banks, buyers and supporting companies were due for consideration on 16 November, but their adoption is not confirmed in the reporting. (Confidence: medium · REPORTED)
- I&W: Estonia confirms the crossings are closed on 1 December and the EU publishes adopted shadow fleet sanctions listings. (0-30 days)
- I&W: The EU formally defers the sanctions decision or France postpones the Paris conference beyond 4 December. (0-30 days)
Outlook & scenarios
Continued low-level pressure with disputed attribution (60%)
It is likely that European authorities continue to report isolated sabotage concerns, reconnaissance and drone alerts, while public evidence remains insufficient to connect every incident to a Russian state direction. Estonia proceeds with its announced border closure and European maritime measures continue without a major expansion in scope.
Containment and improved verification (30%)
It is unlikely that the current incident pattern develops into a sustained campaign. Romanian and Norwegian authorities report no comparable new incidents, while court or forensic disclosures clarify some attributions and European measures remain targeted.
High-impact sabotage incident (10%)
It is very unlikely that a Russian-linked actor carries out a sabotage attack causing fatalities or prolonged disruption at a Norwegian defence, logistics or energy site. If investigators establish Russian direction, European governments face pressure for a coordinated response beyond the measures currently announced.
Recommendations
- Maintain an incident ledger that separates event date, reporting date, location, target, attribution source and disclosed forensic evidence. Record the Larissa 1 report separately until authorities clarify whether it was an additional vessel in the Sulina sequence.
- Prioritise collection on the Threod Systems case: monitor Estonian court filings for evidence behind the GRU attribution, and separately verify whether the announced border closure takes effect on 1 December.
- For the Black Sea, track Romanian maritime warnings, air-force scrambles and official updates on the identities and positions of struck vessels. Do not assign the strikes to Russia unless new evidence or an explicit, evidence-backed attribution emerges.
- Treat the PST warning as a forward-looking threat assessment, not evidence that sabotage has occurred in Norway. Track public updates on reconnaissance, arrests and plots involving defence plants, military suppliers, logistics firms and energy infrastructure.
- Check whether the EU adopted the proposed shadow fleet sanctions and whether the Paris conference proceeds on 4 December. Record implemented measures separately from announcements.
Confidence & uncertainty
Major-media and wire reporting corroborates the Threod Systems attempt, arrests and vessel damage, while official statements provide the main attribution claims and denials. Overall confidence remains medium because public reporting does not disclose evidence establishing GRU or Turla direction, Romania has not identified the source of the Sulina drones, and the Norway warning is detailed here through a single trade-publication account. The reporting also leaves the Sulina incident count and some event dates unresolved.
Intelligence gaps
- [EEI 1.1 · UNCOVERED] Reports, operator notifications, CCTV or satellite imagery showing unexplained physical damage or operational outages at critical infrastructure sites (power substations, gas pipelines/compressor stations, water treatment plants, railway signaling centers, major telecom exchanges). Recommended collection: satellite/imagery
- [EEI 1.2 · PARTIAL] Observed reconnaissance activity around critical sites indicative of attack planning (unauthorised drone flights, repeated surveillance visits, loitering vehicles, mapping/photography of assets). Recommended collection: open-source/media
- [EEI 1.3 · PARTIAL] Law-enforcement or customs seizures, arrests or interdictions of persons or shipments carrying explosives, sabotage tools, specialty cutting/electrical equipment, or covert comms gear destined for/near critical infrastructure. Recommended collection: law enforcement
- [EEI 2.1 · UNCOVERED] Emergence or amplification of coordinated social-media networks (sets of accounts, pages, channels) pushing identical narratives or hashtags across multiple platforms, including bot-like activity metrics and origin IP/common management indicators. Recommended collection: social-media/OSINT
- [EEI 2.2 · UNCOVERED] Publication or internal guidance from state-run media, proxy outlets, or identified influence platforms distributing talking points, pre-scripted messaging, or translated content targeted at specific EU countries/communities. Recommended collection: open-source/media
- [EEI 2.3 · UNCOVERED] Distribution of manipulated multimedia (deepfakes), targeted phishing/whaling campaigns, or localized false narratives timed to political events (elections, protests, court rulings) with tracked reach and engagement metrics. Recommended collection: cyber/forensic
- [EEI 3.1 · UNCOVERED] Unusual financial transactions: wire transfers, crypto conversions, or payments to shell companies, NGOs or individuals exceeding typical baselines that link to known proxies or front organisations. Recommended collection: financial
- [EEI 3.2 · UNCOVERED] Travel and movement indicators for suspected operatives: repeated border crossings, chartered/irregular flights, booking patterns or mobile/location data placing identified individuals in staging areas shortly before incidents. Recommended collection: border/immigration
- [EEI 3.3 · UNCOVERED] Cargo, freight or maritime movements with discrepancies (concealed/dual-use equipment, false manifests, unusual routing) detected at ports, rail hubs or via AIS that correspond to deliveries of material used in sabotage or influence operations. Recommended collection: customs/ports
- [EEI 3.4 · UNCOVERED] Intercepted or otherwise-obtained communications showing tasking, coordination, or payment instructions between Russian agencies/handlers and proxy groups, including identified command-and-control servers or encrypted group identifiers. Recommended collection: signals-intel/SIGINT
Red cell review: CONCUR WITH COMMENT
TLP:CLEAR