TLP:CLEAR · Disclosure is not limited.
Europe Hybrid Threats: New UK Base Breach, Unsettled Attribution
Time window: Last 1 day · Audience: General analyst · Type: Situation report · DTG: 2026-10-09 11:11Z · Overall confidence: HIGH
BLUF
European officials are reporting heightened concern about Russian-linked hybrid activity, but public evidence does not establish a single centrally directed campaign. The RAF Molesworth breach and the RAF Fairford investigation remain separate in police reporting; responsibility for the Molesworth incident is not established, while the UK government has described Fairford as Iran-linked.
Executive summary
UK police arrested two Latvian men, aged 32 and 36, after a reported breach of RAF Molesworth, which hosts US and NATO intelligence centres. Reports disagree whether the intrusion occurred on 7 or 8 October, and police say they have not linked it to the RAF Fairford case. The UK government has said there are strong indications of an Iran-linked plot at Fairford, where seven suspects were arrested and later released on bail or other conditions; the US withdrew B-1 bombers from the base on 4 October. Separately, Denmark’s PET has alleged Russian sabotage operations against Danish defence companies supplying Ukraine, an allegation rejected by the Russian embassy in Copenhagen. The UK and Germany announced a partnership against sabotage and cyberattacks, while reporting says EU ambassadors have discussed the risk of more serious attacks. These developments support heightened monitoring, not confident attribution of every incident to Russia.
Change from previous assessment
Since the 8 October brief, the main new development is the reported RAF Molesworth breach and arrest of two Latvian men. Police have said they do not currently link that case to RAF Fairford, while the UK government has described Fairford as Iran-linked; the distinction is now clearer, but attribution remains unresolved. New reporting also adds Denmark’s PET allegation of sabotage against defence firms supplying Ukraine, EU ambassador discussions about the risk of more serious attacks, and the UK-German partnership announcement. Initial confidence in the broad concern remains steady; confidence in specific Russian attribution remains low where reporting is single-source or disputed.
Key judgments
- It is likely that European officials’ assessments of Russian-linked hybrid pressure are becoming more urgent, but public reporting does not establish one centrally directed campaign. German intelligence warned of a growing threat, the UK government described the threat as spreading, and Denmark’s PET reported a shift from planning towards operations. Those are official assessments and allegations, not independent public verification of each incident. (Confidence: medium · ASSESSED)
- I&W: Confirm: Danish, German or UK authorities publish evidence or charging documents linking specific sabotage incidents to Russian tasking. (0-3 months)
- I&W: Break: Authorities publicly identify the reported incidents as unrelated criminal activity and provide no evidence of foreign direction. (0-3 months)
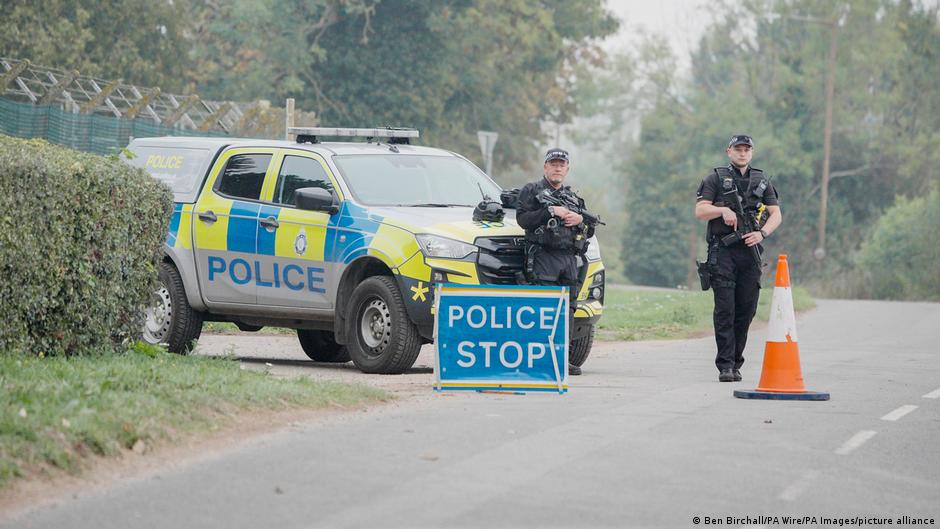
- The RAF Molesworth breach is a reported security incident involving two Latvian men, but public reporting does not establish Russian direction or a connection to RAF Fairford. The men were reported to have damaged the perimeter fence and were arrested on suspicion of offences under the UK National Security Act. Accounts place the intrusion on either 7 or 8 October, leaving the timeline unresolved. Police have said they do not currently link the Molesworth investigation to Fairford; the UK government’s Iran-linked assessment concerns Fairford, not an established attribution for Molesworth. (Confidence: medium · REPORTED)
- I&W: Confirm a foreign link: UK police or prosecutors publicly identify a Russian handler, tasking or financing in charges relating to the Molesworth breach. (0-30 days)
- I&W: Break a foreign-link hypothesis: charging information identifies only trespass or property damage and police state that the investigation has found no foreign direction. (0-3 months)
- The PET allegation of Russian sabotage against Danish defence companies supplying Ukraine warrants attention, but the public evidence is too thin to establish Russian responsibility independently. The account rests on a PET representative’s statements, and the Russian embassy in Copenhagen rejected the accusation. Confidence in the specific attribution is low. (Confidence: low · REPORTED)
- I&W: Confirm: Danish authorities file charges or release forensic evidence connecting a specific attack, surveillance task or recruited intermediary to Russian direction. (0-3 months)
- I&W: Break: Danish authorities state that the reported activity did not target defence companies or was not directed by a foreign actor. (0-3 months)
- The UK-German partnership is likely to improve coordination against sabotage and cyber threats if its announced information-sharing and joint-action plans are implemented. Current reporting establishes the announcement and stated aims, not operational results. (Confidence: medium · ASSESSED)
- I&W: Confirm: London and Berlin announce a shared reporting channel, joint investigation procedures or a named coordination mechanism for infrastructure incidents. (0-3 months)
- I&W: Break: Neither government reports an operational step or joint activity under the partnership by the end of the next quarter. (1-3 months)
- A hybrid attack causing mass casualties is unlikely in the near term, but it remains a low-probability, high-impact warning scenario. Reporting says EU ambassadors have discussed the risk of more serious attacks after an explosives-laden drone was found at Leipzig airport in August. Public reporting does not establish that the Leipzig device was part of a Russian operation; the reported GRU attribution is not independently substantiated in the available claims. (Confidence: low · ASSESSED)
- I&W: Confirm: German authorities publicly report a further explosives-bearing device or a charged plot targeting a transport hub or other civilian site. (0-3 months)
- I&W: Break: German authorities publish findings that rule out an operational explosive device or foreign-directed plot in the Leipzig case. (0-3 months)
Outlook & scenarios
Persistent pressure, contested attribution (62%)
This is the most likely course. European governments continue to report hybrid threats, while public evidence remains uneven and individual cases retain separate or unresolved attribution. The UK-German partnership advances information exchange, but its operational effect is not yet clear.
Evidence links further incidents to Russian tasking (28%)
Danish or other European authorities publish charges or evidence connecting specific sabotage activity to Russian direction. That would strengthen the case for a pattern of Russian-linked operations, while still not by itself proving a single central command structure.
Low-probability, high-impact attack (8%)
A plot against a civilian site or transport hub causes mass casualties and prompts a sharper European response. Current reporting records official concern about this outcome, but does not establish an imminent plot or confirm Russian responsibility for the Leipzig airport device.
Recommendations
- Keep RAF Molesworth and RAF Fairford as separate incident files. Record the disputed Molesworth date and preserve the distinction between the UK government’s Iran-linked Fairford assessment and police statements about the relationship between the two cases.
- Track UK police and prosecutorial updates on the two Latvian suspects, including any publicly stated motive, foreign contact or evidence supporting the suspected National Security Act offences.
- Treat the Danish PET account as an allegation pending corroboration. Monitor for charges, forensic evidence or official clarification, and record the Russian embassy’s denial alongside the original claim.
- Request or monitor concrete implementation details from the UK-German partnership, especially shared reporting procedures and joint activity concerning critical infrastructure.
- Track German authority updates on the Leipzig airport drone separately from claims of GRU involvement. Do not present the attribution as established without public supporting evidence.
Confidence & uncertainty
Overall confidence is high in the broad picture of heightened official concern and an active European response. UK, German and Danish official statements, alongside reporting of the Molesworth arrests and EU ambassador discussions, provide corroboration for that picture. Confidence is lower on responsibility for specific incidents: the Danish sabotage allegation is disputed and thinly corroborated, the Molesworth timeline conflicts, and public reporting does not establish a Russian link to that breach or to the Leipzig device.
Alternative analysis (red cell)
Public reporting supports heightened official concern about the possibility of more serious hybrid attacks, but it does not permit a robust estimate that a mass-casualty event is unlikely in the near term. The Leipzig evidence is low-grade (c86341f7-dff9-4814-9a09-4d92cd276290), and the reported GRU attribution is not independently established (af95f2c1-eb1f-4032-bc20-f4185d6d2b80). A more defensible reading is that the scenario is insufficiently quantified rather than demonstrably low probability.
Intelligence gaps
- [EEI 1.2 · PARTIAL] Observed reconnaissance activity around critical sites indicative of attack planning (unauthorised drone flights, repeated surveillance visits, loitering vehicles, mapping/photography of assets). Recommended collection: open-source/media
- [EEI 1.3 · PARTIAL] Law-enforcement or customs seizures, arrests or interdictions of persons or shipments carrying explosives, sabotage tools, specialty cutting/electrical equipment, or covert comms gear destined for/near critical infrastructure. Recommended collection: law enforcement
- [EEI 2.1 · UNCOVERED] Emergence or amplification of coordinated social-media networks (sets of accounts, pages, channels) pushing identical narratives or hashtags across multiple platforms, including bot-like activity metrics and origin IP/common management indicators. Recommended collection: social-media/OSINT
- [EEI 2.2 · UNCOVERED] Publication or internal guidance from state-run media, proxy outlets, or identified influence platforms distributing talking points, pre-scripted messaging, or translated content targeted at specific EU countries/communities. Recommended collection: open-source/media
- [EEI 2.3 · UNCOVERED] Distribution of manipulated multimedia (deepfakes), targeted phishing/whaling campaigns, or localized false narratives timed to political events (elections, protests, court rulings) with tracked reach and engagement metrics. Recommended collection: cyber/forensic
- [EEI 3.1 · UNCOVERED] Unusual financial transactions: wire transfers, crypto conversions, or payments to shell companies, NGOs or individuals exceeding typical baselines that link to known proxies or front organisations. Recommended collection: financial
- [EEI 3.2 · UNCOVERED] Travel and movement indicators for suspected operatives: repeated border crossings, chartered/irregular flights, booking patterns or mobile/location data placing identified individuals in staging areas shortly before incidents. Recommended collection: border/immigration
- [EEI 3.3 · PARTIAL] Cargo, freight or maritime movements with discrepancies (concealed/dual-use equipment, false manifests, unusual routing) detected at ports, rail hubs or via AIS that correspond to deliveries of material used in sabotage or influence operations. Recommended collection: customs/ports
- [EEI 3.4 · UNCOVERED] Intercepted or otherwise-obtained communications showing tasking, coordination, or payment instructions between Russian agencies/handlers and proxy groups, including identified command-and-control servers or encrypted group identifiers. Recommended collection: signals-intel/SIGINT
Cited sources
[1] Deutsche Welle (DW) · Берлин и Лондон на фоне роста российской гибридной угрозы запустят партнерство против кибератак (A) · 8 October 2026 · sha256:3d92b2729117 [2] Eesti Rahvusringhääling (ERR) · Германия и Британия будут сотрудничать в противодействии кибератакам и саботажу (A) · 8 October 2026 · sha256:82c329635fc3 [3] UNIAN · РФ изменила тактику: в Дании заявили о диверсиях против производителей оружия для Украины (B) · 8 October 2026 · sha256:8b475e80b1ed [4] Gordon (gordonua.com) · В день конференции, посвященной РФ. Двое граждан Латвии проникли на территорию "жемчужины" разведки НАТО (B) · 9 October 2026 · sha256:05ef332ff3ca [5] Deutsche Welle (DW) · В Великобритании задержали двух граждан Латвии после проникновения на авиабазу Моулсворт (A) · 8 October 2026 · sha256:2e0ea52afce4 [6] The i Paper (inews.co.uk) · A ‘multiple casualty’ hybrid attack by Russia is Europe’s new worst-case scenario (A) · 9 October 2026 · sha256:baf57ff8107d
Source content hashes were computed at collection time; the cited text is preserved unmodified for the life of this product.
Red cell review: PARTIAL DISSENT
TLP:CLEAR