TLP:CLEAR · Disclosure is not limited.
Europe Hybrid Threats: Sabotage Allegations and Black Sea Attacks
Time window: Last 1 day · Audience: General analyst · Type: Situation report · DTG: 2026-10-29 14:13Z · Overall confidence: HIGH
BLUF
Reporting widens the threat picture beyond Romania’s Brașov case: the European Commission is reported to have verified a failed Russian operation at Leipzig/Halle, and drone attacks on merchant shipping off Bulgaria add a second security concern. Attribution is stronger for Leipzig than for the Brașov fire, the Munich incendiary-device allegation or the Black Sea attacks; the supplied reporting does not establish one Russian-directed disinformation campaign spanning separate incidents.
Executive summary
Since the prior brief, reporting has added an alleged Russian operation at Leipzig/Halle Airport, which the European Commission is reported to have verified, and an attack by three sea drones on a Greek-owned, Liberian-flagged container ship 21 miles south-east of Shabla, Bulgaria, on 28 October. Romanian authorities continue to attribute the 14 September Brașov fire to a Russia-directed network; three foreign nationals are under investigation, while Russia rejects the allegation. The evidence for separate disinformation-related incidents in Ceuta, the UK and Paris remains thin, and reporting does not show that they were centrally directed as one campaign.
Change from previous assessment
Since the 28 October brief, the assessment has widened beyond the Brașov investigation. New reporting says the European Commission verified the failed Leipzig/Halle operation as Russian and adds detail on the 28 October sea-drone attack off Shabla and repeated attacks on commercial vessels in the western Black Sea. The Brașov case remains unresolved on Russian state direction and the fire’s precise target; the assessment of a single cross-country disinformation campaign remains low confidence.
Key judgments
- Russia-linked sabotage activity in Europe is likely to remain a live threat to defence and related sites, but attribution is uneven. Reporting says the European Commission verified the failed August operation at Leipzig/Halle as Russian; Romanian authorities attribute the 14 September fire near CARFIL SA in Brașov to a Russia-directed network, while the Russian Embassy rejects the allegation. The report of incendiary devices at Rohde & Schwarz and Helsing offices in Munich remains a single-publication allegation. Confidence is medium because the reporting includes official Romanian statements and reported Commission verification, but the Brașov attribution is disputed and the Munich allegation lacks corroboration. (Confidence: medium · ASSESSED)
- I&W: German or Romanian prosecutors publish charges or evidence linking suspects to additional planned attacks on defence or industrial sites, confirming the reported network activity; official withdrawal of the Brașov attribution or court findings excluding a Russia-linked network would weaken this judgment. (1-3 months)
- I&W: German authorities publish forensic findings on the reported Munich devices or the Leipzig/Halle operation, confirming or rejecting Russian involvement. (0-3 months)
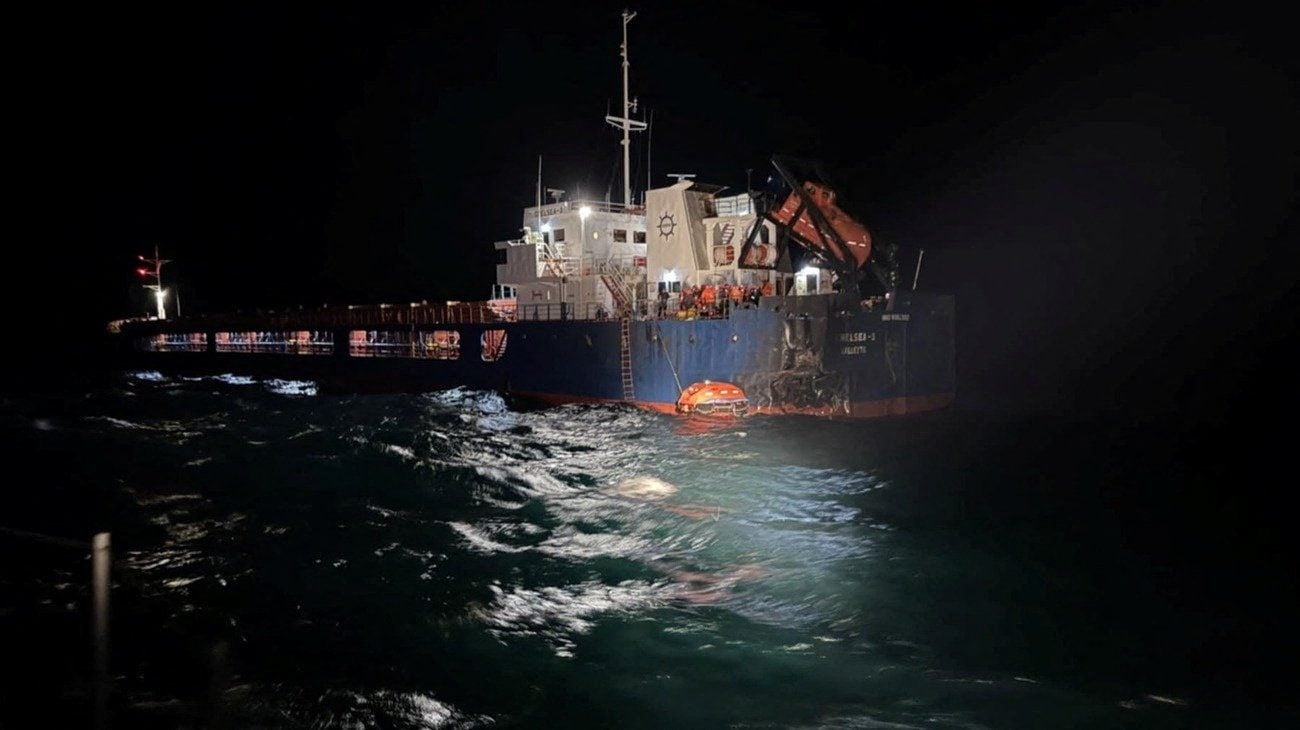
- Further drone attacks on commercial shipping off Bulgaria and Romania are likely in the next 1-3 months, but responsibility for the attacks remains unresolved. On 28 October, three sea drones struck a Greek-owned, Liberian-flagged container ship about 21 miles south-east of Shabla; all 18 crew were evacuated. Reporting also describes at least six merchant vessels attacked off Bulgaria in recent weeks and likely deaths among about two dozen seafarers. Ukraine has accused Russia, Moscow denies involvement, and reporting on Bulgarian President Rumen Radev’s position conflicts. Confidence is medium: the attack and evacuation are corroborated by the ship’s owner and Bulgarian authorities, while attribution is contested. (Confidence: medium · ASSESSED)
- I&W: Bulgarian or Romanian authorities report another drone strike on a named commercial vessel in their Black Sea exclusive economic zone, confirming continued attacks; a sustained period without reported attacks would weaken the forecast. (0-14 days)
- I&W: Authorities publish forensic findings identifying or excluding a Russian operator in the 28 October attack off Shabla, resolving or further substantiating the attribution dispute. (0-3 months)
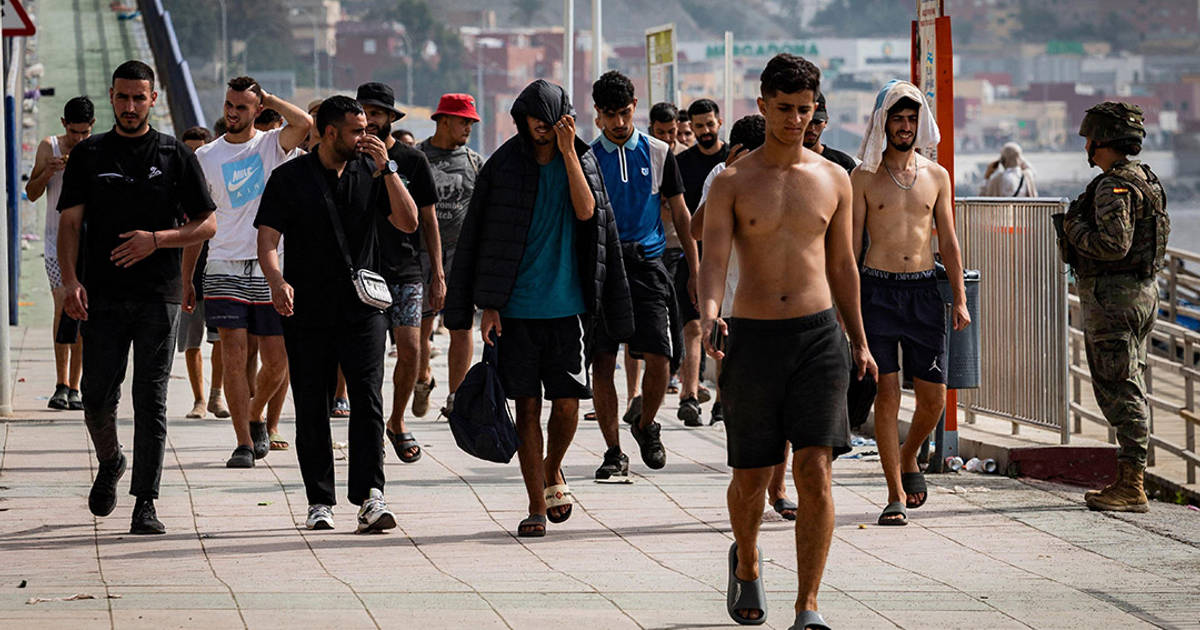
- It is unlikely that the supplied reporting establishes one Russian-directed campaign linking the Ceuta migration episode, the arson attack on the former UK Prime Minister’s private residence and the placement of pigs’ heads at nine Parisian mosques. A separate claim of coordinated Russian social-media manipulation targeting Ukrainians in Poland is also uncorroborated here. These accounts rest on thin, largely single-source reporting, so confidence is low. (Confidence: low · ASSESSED)
- I&W: A government investigation or independently corroborated platform analysis identifies common Russian-linked organisers, infrastructure or funding across the named incidents, strengthening the case for a coordinated campaign. (1-3 months)
- I&W: Official investigations identify domestic or unrelated perpetrators for the Ceuta, UK or Paris incidents, weakening the case for common Russian direction. (1-6 months)
Outlook & scenarios
Continued deniable pressure on European targets (55%)
Russian-linked activity remains focused on sabotage or attempted sabotage involving defence industry and transport-related sites. The Brașov investigation and the reported Leipzig/Halle operation remain central cases, while authorities examine whether the Munich allegation has a verified basis.
Maritime attacks prompt stronger regional protection (30%)
Further drone attacks disrupt commercial shipping near Bulgaria or Romania. Bulgarian, Romanian and Turkish officials increase coordination and maritime monitoring, while disagreement over responsibility limits a common public attribution.
High-impact attack raises the stakes (10%)
A low-probability, high-impact outcome is a lethal attack on a European defence executive or a serious strike on a defence-industry site. The warning attributed to representatives of five EU intelligence agencies and Maria Zakharova’s statement that European defence industries supplying Ukraine are legitimate targets give this scenario a basis, but do not establish an imminent attack.
Recommendations
- Track the Brașov investigation separately from Romanian public attribution. Record the legal status of the three suspects, any extradition decisions, and evidence released by DIICOT or the Bucharest Court of Appeal.
- For the Leipzig/Halle and Munich cases, distinguish reported official verification from single-publication allegations. Seek public statements from the European Commission and German investigators before treating the cases as equally substantiated.
- Maintain a dated incident log for commercial-vessel attacks in the Bulgarian and Romanian Black Sea zones. Record vessel name, flag, location, weapon type, casualties, official attribution and any forensic findings.
- Do not combine the Ceuta, UK, Paris and Poland claims into a single campaign assessment without corroboration. Check for common operators, accounts, funding or infrastructure before making that link.
- Review the reporting on Rumen Radev’s statements against his original remarks before using them to characterise Bulgaria’s position on Russian responsibility for Black Sea attacks.
Confidence & uncertainty
Overall confidence is high in the reported event picture because the Romanian case includes official intelligence and prosecutorial statements, the Shabla attack is reported by a wire service and corroborated by Bulgarian authorities and the ship’s owner, and the Leipzig/Halle attribution is reported as a European Commission verification. Confidence in Russian responsibility is more variable: the Brașov allegation is denied by Russia, the Munich report lacks independent corroboration, and attribution for the Black Sea attacks is contested. The disinformation claims remain thin and largely single-source.
Intelligence gaps
- [EEI 1.2 · UNCOVERED] Observed reconnaissance activity around critical sites indicative of attack planning (unauthorised drone flights, repeated surveillance visits, loitering vehicles, mapping/photography of assets). Recommended collection: open-source/media
- [EEI 1.3 · UNCOVERED] Law-enforcement or customs seizures, arrests or interdictions of persons or shipments carrying explosives, sabotage tools, specialty cutting/electrical equipment, or covert comms gear destined for/near critical infrastructure. Recommended collection: law enforcement
- [EEI 2.1 · UNCOVERED] Emergence or amplification of coordinated social-media networks (sets of accounts, pages, channels) pushing identical narratives or hashtags across multiple platforms, including bot-like activity metrics and origin IP/common management indicators. Recommended collection: social-media/OSINT
- [EEI 2.2 · PARTIAL] Publication or internal guidance from state-run media, proxy outlets, or identified influence platforms distributing talking points, pre-scripted messaging, or translated content targeted at specific EU countries/communities. Recommended collection: open-source/media
- [EEI 2.3 · PARTIAL] Distribution of manipulated multimedia (deepfakes), targeted phishing/whaling campaigns, or localized false narratives timed to political events (elections, protests, court rulings) with tracked reach and engagement metrics. Recommended collection: cyber/forensic
- [EEI 3.1 · UNCOVERED] Unusual financial transactions: wire transfers, crypto conversions, or payments to shell companies, NGOs or individuals exceeding typical baselines that link to known proxies or front organisations. Recommended collection: financial
- [EEI 3.2 · UNCOVERED] Travel and movement indicators for suspected operatives: repeated border crossings, chartered/irregular flights, booking patterns or mobile/location data placing identified individuals in staging areas shortly before incidents. Recommended collection: border/immigration
- [EEI 3.3 · UNCOVERED] Cargo, freight or maritime movements with discrepancies (concealed/dual-use equipment, false manifests, unusual routing) detected at ports, rail hubs or via AIS that correspond to deliveries of material used in sabotage or influence operations. Recommended collection: customs/ports
- [EEI 3.4 · UNCOVERED] Intercepted or otherwise-obtained communications showing tasking, coordination, or payment instructions between Russian agencies/handlers and proxy groups, including identified command-and-control servers or encrypted group identifiers. Recommended collection: signals-intel/SIGINT
Red cell review: CONCUR WITH COMMENT
TLP:CLEAR