TLP:CLEAR · Disclosure is not limited.
Europe: Russian Hybrid Threats and Attribution Gaps
Time window: Last 1 day · Audience: General analyst · Type: Situation report · DTG: 2026-10-26 17:12Z · Overall confidence: HIGH
BLUF
Russian hybrid pressure on European states is likely to persist, but the supplied reporting does not establish Russian direction of the named sabotage cases or a current centrally directed disinformation campaign. Black Sea shipping faces a continuing risk of disruption, while responsibility for the Khoryv sinking remains unresolved.
Executive summary
UK security and defence officials have warned of escalating Russian hybrid activity, while reporting on specific European incidents remains uneven. The Italy weapons-factory explosion, Bulgaria factory fire and foiled drone attack at Leipzig airport are attributed to unknown actors in the supplied reporting; the alleged GRU-linked network in Slovakia is cited through political comment on German media reports. Separate reporting says Russia continued attacks on Ukraine, and the FSB announced that it had foiled an alleged Ukrainian drone plot in Moscow. These reports describe distinct events and do not establish Russian responsibility for sabotage in Europe. In the Black Sea, the Khoryv sent a distress call after a drone attack off Constanța on 23 October, but the operator has not been identified in the supplied claims.
Change from previous assessment
Since the 25 October brief, reporting adds the FSB’s 26 October claim that it foiled an alleged SBU drone plot against air-defence and electricity facilities in Moscow and detained two men. That allegation does not establish Russian direction of sabotage in Europe, so the prior low-confidence assessment of those European cases remains unchanged. New reporting also records NATO’s announced Black Sea patrol and forensic deployment; the assessment of shipping risk remains active, while responsibility for the Khoryv attack is still unresolved. The prior assessment of protest-related narrative amplification was not updated by new event-specific evidence in this run.
Key judgments
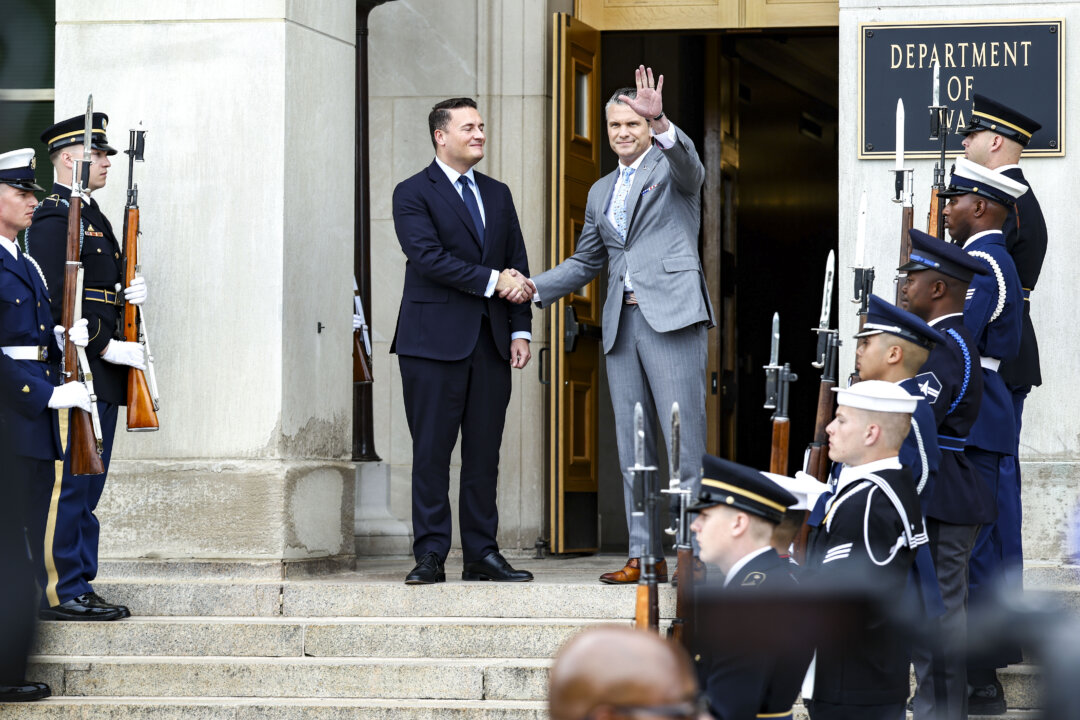
- Russian state-linked hybrid pressure on European countries is likely to persist over the next 1-3 months, but senior UK warnings do not establish responsibility for each reported incident. MI5 Director General Ken McCallum said Russian military and intelligence services were escalating hybrid warfare below the NATO Article V threshold, and Defence Secretary Wes Streeting described a Russian campaign across Europe. These are official warnings, not public evidence linking Russia to the specific incidents in this brief. (Confidence: medium · ASSESSED)
- I&W: Confirming indicator: a European government or court publicly attributes a new sabotage or cyber incident to a named Russian state service and releases operational evidence linking the service to the activity. (0-3 months)
- I&W: Breaking indicator: investigators publicly attribute one of the cited incidents to a non-state actor or accidental cause, and report no Russian tasking or support. (1-3 months)
- It is unlikely that the supplied reporting establishes Russian direction of the reported Italy, Bulgaria, Leipzig or Slovakia cases. A weapons factory in Italy was reportedly damaged by an explosion, a Bulgarian weapons factory by fire, and a drone attack on a Ukraine resupply aircraft at Leipzig airport was reportedly foiled; the reporting identifies the actors as unknown. Veronika Remišová cited German media reports of an alleged GRU-linked sabotage network directed from Slovakia, but the supplied claim does not provide independent evidence of that link. Confidence is low because these accounts rely on think-tank or political reporting rather than corroborated investigative findings. (Confidence: low · ASSESSED)
- I&W: Confirming indicator: police or prosecutors in Italy, Bulgaria, Germany or Slovakia report that a cited case remains unattributed or that evidence does not establish foreign direction. (1-3 months)
- I&W: Breaking indicator: a court filing or official investigation names a Russian service or handler and discloses evidence connecting it to one of the cited cases. (1-3 months)
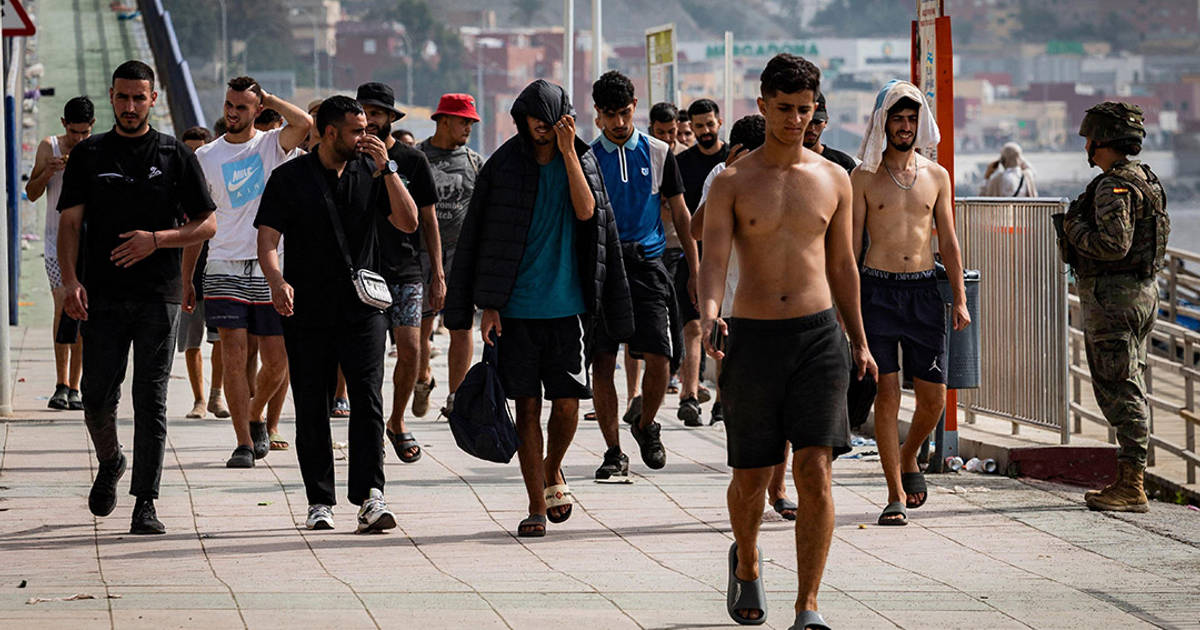
- It is unlikely that the supplied claims establish a current, centrally directed Russian disinformation campaign targeting European unrest. A think-tank account attributes disinformation to the movement of more than 70,000 young Moroccans onto Ceuta beach, and another describes a Russian campaign amplifying an arson attack on the then British Prime Minister’s residence. A separate account says pigs’ heads were placed outside nine Paris mosques to fuel interreligious tension, but identifies the actor as unknown. These examples are thinly corroborated and do not establish a current coordinated campaign across Europe. (Confidence: low · ASSESSED)
- I&W: Breaking indicator: a platform investigation or European authority publishes forensic evidence linking coordinated accounts amplifying one of the named incidents to Russian state infrastructure or operators. (0-3 months)
- I&W: Confirming indicator: a public investigation attributes amplification of a named incident to domestic actors or organic sharing and reports no evidence of Russian coordination. (1-3 months)
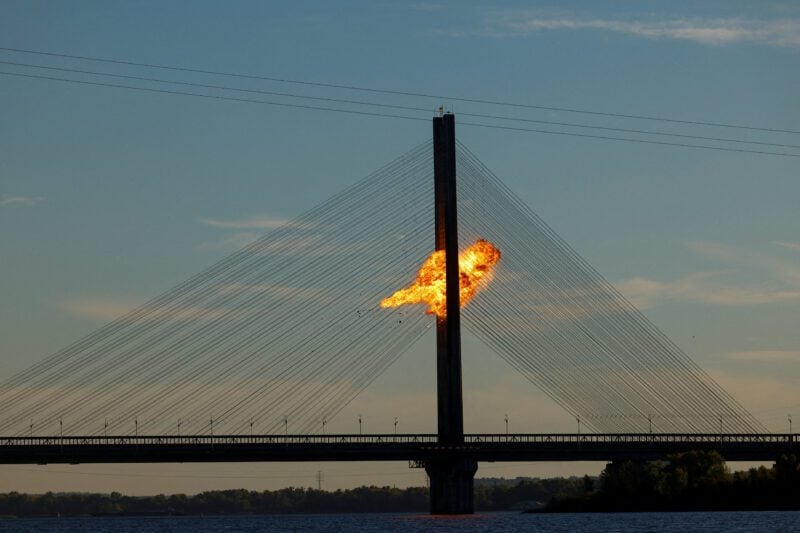
- Further disruption to Black Sea commercial shipping is likely over the next month, but responsibility for the 23 October drone attack on the Khoryv remains unresolved. The vessel sent a distress call 13 nautical miles off Constanța after the attack. Bulgarian Prime Minister Rumen Radev said the attacks’ logic pointed to Moscow but also said Bulgaria could not prove responsibility. Russia’s Defence Ministry claimed strikes on cargo vessels bound for Chornomorsk and Odesa; Reuters reported that it could not independently verify the ministry’s information. Ukrainian maritime drone activity and the announced NATO deployment of patrol aircraft, radar, drones, intelligence personnel and forensic teams form relevant alternative context, not proof of who struck the Khoryv. (Confidence: low · ASSESSED)
- I&W: Confirming indicator: another named merchant vessel reports a drone strike or sends a distress call in the Black Sea, or NATO forensic teams publicly report new explosive evidence from a vessel attack. (0-30 days)
- I&W: Breaking indicator: Romanian authorities or NATO publish forensic findings identifying the operator responsible for the Khoryv attack. (1-3 months)
Outlook & scenarios
Continued pressure, unresolved attribution (60%)
Russian-linked cyber and influence activity is likely to continue below the threshold of direct armed conflict, while European investigations leave the named sabotage cases unresolved. Black Sea shipping incidents persist, but public evidence does not settle responsibility for the Khoryv attack.
European investigations establish a Russian link (25%)
It is unlikely but plausible that a European investigation publishes evidence connecting a Russian state service or its intermediaries to one of the cited sabotage cases. That finding would strengthen the case for coordinated Russian activity and increase pressure for a common European response.
High-impact disruption to essential services (8%)
A low-probability, high-impact scenario is a physical attack on infrastructure that interrupts essential services or causes casualties. The supplied reporting does not establish such an operation, but UK preparedness measures and reports of attacks on European-linked targets make this a relevant warning scenario.
Recommendations
- Keep confirmed incident facts separate from attribution claims in reporting. Label the FSB account of the alleged Moscow plot, the Slovakia GRU allegation and the Black Sea vessel claims by source and evidentiary status.
- Track public case developments in Italy, Bulgaria, Germany and Slovakia. Prioritise indictments, court filings, forensic findings and statements from the investigating authorities over political commentary or second-hand summaries.
- For disinformation reporting, require dated examples and evidence of coordinated account behaviour or operational links before assessing a campaign as centrally directed. Record whether amplification is attributable, merely alleged or unknown.
- Monitor Romanian and NATO updates on the Khoryv investigation, alongside reports of new named vessel incidents in the Black Sea. Do not treat Russian Defence Ministry claims or Bulgaria’s unproven attribution as independently verified findings.
- Review the UK and Polish official statements on hybrid threats against the specific incidents cited in this brief. Record any new public evidence that links a named incident to Russian state services.
Confidence & uncertainty
Overall confidence is high for the broad situation picture because official UK statements and major-media reporting support the reporting of continued Russian attacks on Ukraine, and the main threat warnings are directly attributed to named UK officials. This confidence applies to the reported events and statements, not to the attribution of individual European sabotage or disinformation cases. Those attributions rely on thin, second-hand or single-source accounts, and the Khoryv operator remains unidentified in the supplied reporting.
Intelligence gaps
- [EEI 1.2 · UNCOVERED] Observed reconnaissance activity around critical sites indicative of attack planning (unauthorised drone flights, repeated surveillance visits, loitering vehicles, mapping/photography of assets). Recommended collection: open-source/media
- [EEI 2.1 · UNCOVERED] Emergence or amplification of coordinated social-media networks (sets of accounts, pages, channels) pushing identical narratives or hashtags across multiple platforms, including bot-like activity metrics and origin IP/common management indicators. Recommended collection: social-media/OSINT
- [EEI 2.2 · UNCOVERED] Publication or internal guidance from state-run media, proxy outlets, or identified influence platforms distributing talking points, pre-scripted messaging, or translated content targeted at specific EU countries/communities. Recommended collection: open-source/media
- [EEI 2.3 · UNCOVERED] Distribution of manipulated multimedia (deepfakes), targeted phishing/whaling campaigns, or localized false narratives timed to political events (elections, protests, court rulings) with tracked reach and engagement metrics. Recommended collection: cyber/forensic
- [EEI 3.1 · PARTIAL] Unusual financial transactions: wire transfers, crypto conversions, or payments to shell companies, NGOs or individuals exceeding typical baselines that link to known proxies or front organisations. Recommended collection: financial
- [EEI 3.2 · PARTIAL] Travel and movement indicators for suspected operatives: repeated border crossings, chartered/irregular flights, booking patterns or mobile/location data placing identified individuals in staging areas shortly before incidents. Recommended collection: border/immigration
- [EEI 3.3 · UNCOVERED] Cargo, freight or maritime movements with discrepancies (concealed/dual-use equipment, false manifests, unusual routing) detected at ports, rail hubs or via AIS that correspond to deliveries of material used in sabotage or influence operations. Recommended collection: customs/ports
Red cell review: CONCUR WITH COMMENT
TLP:CLEAR