TLP:CLEAR · Disclosure is not limited.
Europe: Russian Hybrid Threats and Romania’s Carfil Investigation
Time window: Last 1 day · Audience: General analyst · Type: Situation report · DTG: 2026-10-27 13:30Z · Overall confidence: HIGH
BLUF
Romanian authorities have publicly linked a suspected sabotage network to Russia and the 14 September fire or explosion at the Carfil industrial platform near Brașov, a new attribution that raises the salience of the threat but does not settle disputed details or establish the wider pattern. The UK-Poland Warsaw Defence Plan and renewed E5 warnings show a stronger public focus on deterrence and counter-drone cooperation.
Executive summary
On 26 October, Romania’s DIICOT and SRI said three foreign nationals, two Belarusians and one Ukrainian, were linked to a sabotage network coordinated from Russia and involved in an incident at the Carfil industrial site near Brașov. Romanian prosecutors are seeking the three suspects’ extradition from Germany and Poland. Reporting differs on whether the incident was an explosion or fire, whether the factory itself was damaged, and whether the case is described as completed or attempted sabotage. Separately, the E5 Defence Ministers and German Defence Minister Boris Pistorius warned of Russian hybrid activity, while the UK and Poland announced plans for expanded defence cooperation, including counter-drone work and a large exercise in Poland next month. The supplied claims still do not establish a centrally directed Russian disinformation campaign across Europe.
Change from previous assessment
Since the 26 October brief, the main change is Romania’s public attribution of the Carfil industrial-site incident to a network said by DIICOT and SRI to be coordinated from Russia, alongside reported extradition requests for three suspects. This adds a named official attribution absent from the prior brief, but the fire-versus-explosion and attempted-versus-completed descriptions remain unresolved. The E5 statement and Pistorius’s warning add current official assessments of escalating hybrid pressure. The UK-Poland Warsaw Defence Plan is a new announced response. The assessment that the supplied reporting does not establish a centrally directed European disinformation campaign remains unchanged.
Key judgments
- Russian hybrid pressure on European states is likely to persist over the next 1-3 months. On 26 October, the E5 Defence Ministers said Russia was committing sabotage and increasingly using multi-domain hybrid attacks; on 27 October, Boris Pistorius warned that Russian hybrid attacks against European targets were escalating. The Danish Defence Intelligence Service’s September assessment also forecast further intensification. These are mutually reinforcing official warnings, but they do not independently establish Russian responsibility for every reported incident. (Confidence: medium · ASSESSED)
- I&W: A European security service publicly attributes a new, specific sabotage, cyber or drone incident to Russian direction. (1-3 months)
- I&W: By 27 January 2027, no additional European authority reports a Russian-linked incident and a national intelligence service revises its near-term hybrid threat forecast downwards. (1-3 months)
- Romanian authorities have publicly attributed the Carfil case to a Russia-coordinated network, but the supplied reporting does not resolve the incident’s precise nature or legal status. DIICOT and SRI said three foreign nationals, two Belarusians and one Ukrainian, were involved in an explosion at the Carfil industrial site in Brașov; separate reporting says prosecutors are seeking their extradition from Germany and Poland in an attempted-sabotage case. Other accounts describe a fire at the industrial platform near the weapons manufacturer, rather than confirming that the factory itself burned. The official attribution is consequential, but these discrepancies lower confidence in the details and do not amount to independent proof of Russian direction. (Confidence: medium · REPORTED)
- I&W: DIICOT or a court publishes an indictment or filing that presents evidence linking the suspects to Russian tasking, communications or financing. (0-3 months)
- I&W: A Romanian court filing or official statement withdraws the Russian-coordination allegation or identifies a non-Russian organiser. (0-3 months)
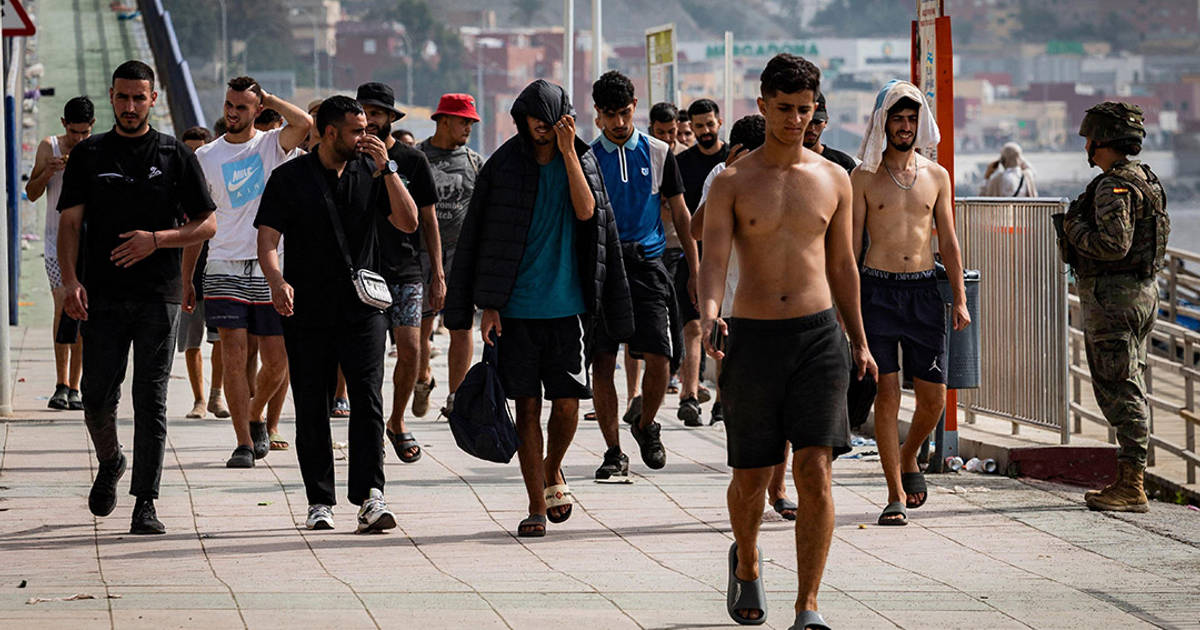
- It is unlikely that the supplied reporting establishes a centrally directed Russian disinformation campaign spanning Europe. The examples include a think-tank claim that disinformation encouraged more than 70,000 young Moroccans to reach Ceuta, an alleged campaign amplifying an arson attack on a former UK Prime Minister’s residence, and claims of Russian social media manipulation in Poland. These accounts lack public forensic evidence or independent corroboration tying the separate cases to common Russian direction; the Paris mosque incident is attributed to unknown perpetrators. (Confidence: low · ASSESSED)
- I&W: An independent technical investigation or platform transparency report links two or more named European cases to shared Russian-controlled accounts, infrastructure or tasking. (1-3 months)
- I&W: Independent investigations identify unrelated actors or domestic motives in the named cases and find no shared account network or direction. (1-3 months)
- The UK and Poland have announced a concrete expansion of defence cooperation, but the supplied reporting describes planned activity rather than proof of new deployed capabilities. The Warsaw Defence Plan covers sea, land, air, cyber and industry; the two governments also announced increased Baltic Sea maritime activity, joint drone and counter-drone development, and a Coalition of the Willing exercise in Poland next month involving thousands of personnel. (Confidence: medium · REPORTED)
- I&W: The UK or Polish government publishes an exercise schedule or after-action report confirming the November exercise took place and giving personnel numbers. (0-2 months)
- I&W: Either government announces that the exercise is postponed or cancelled, or that the planned Baltic maritime or counter-drone work has been suspended. (0-2 months)
Outlook & scenarios
Continued hybrid pressure and stronger public attribution (60%)
Russian-linked hybrid activity remains a prominent European security concern over the next 1-3 months. European governments continue to issue warnings and investigate incidents, while the UK-Poland plan advances through exercises and counter-drone cooperation. This is the most likely course, but the public evidence continues to vary by incident.
Romania’s investigation produces corroborating evidence (30%)
Romanian prosecutors’ extradition requests lead to court proceedings that clarify the Carfil incident and the alleged network’s links to Russia. Further official reporting confirms the suspects’ roles or identifies additional targets. This would strengthen the case-specific attribution, without by itself proving that separate European incidents form one centrally directed campaign.
High-impact escalation against critical infrastructure (10%)
An unlikely but high-impact scenario is a further sabotage or drone incident causing confirmed damage to a European defence or critical infrastructure site, followed by public evidence of Russian tasking. Such a development would sharpen pressure on NATO allies to coordinate attribution and response.
Recommendations
- Track DIICOT and SRI statements, Romanian court filings, and extradition proceedings in Germany and Poland. Record separately the evidence for Russian direction, the suspects’ alleged roles, and whether the incident is classified as completed or attempted sabotage.
- Do not treat the Carfil case as proof of a Europe-wide campaign. Compare any new official attributions with independently reported evidence before linking incidents across countries.
- Monitor UK and Polish government announcements for the November exercise schedule, personnel numbers, Baltic Sea activity and milestones in joint drone and counter-drone development.
- For disinformation claims, prioritise platform data, independent network analysis and named investigative findings. Distinguish evidence of amplification from evidence of Russian state direction.
Confidence & uncertainty
Overall confidence is high in the broad situation picture: official E5 and Romanian statements, UK government announcements, and major-media or wire reporting establish that European governments are treating hybrid threats as an active concern and are announcing concrete defence responses. Confidence is lower in individual attribution details. The Carfil accounts differ on the nature and extent of the damage and the legal characterisation, while the supplied disinformation examples are thinly corroborated and do not establish central direction.
Intelligence gaps
- [EEI 1.2 · PARTIAL] Observed reconnaissance activity around critical sites indicative of attack planning (unauthorised drone flights, repeated surveillance visits, loitering vehicles, mapping/photography of assets). Recommended collection: open-source/media
- [EEI 1.3 · PARTIAL] Law-enforcement or customs seizures, arrests or interdictions of persons or shipments carrying explosives, sabotage tools, specialty cutting/electrical equipment, or covert comms gear destined for/near critical infrastructure. Recommended collection: law enforcement
- [EEI 2.1 · PARTIAL] Emergence or amplification of coordinated social-media networks (sets of accounts, pages, channels) pushing identical narratives or hashtags across multiple platforms, including bot-like activity metrics and origin IP/common management indicators. Recommended collection: social-media/OSINT
- [EEI 2.2 · UNCOVERED] Publication or internal guidance from state-run media, proxy outlets, or identified influence platforms distributing talking points, pre-scripted messaging, or translated content targeted at specific EU countries/communities. Recommended collection: open-source/media
- [EEI 2.3 · PARTIAL] Distribution of manipulated multimedia (deepfakes), targeted phishing/whaling campaigns, or localized false narratives timed to political events (elections, protests, court rulings) with tracked reach and engagement metrics. Recommended collection: cyber/forensic
- [EEI 3.1 · UNCOVERED] Unusual financial transactions: wire transfers, crypto conversions, or payments to shell companies, NGOs or individuals exceeding typical baselines that link to known proxies or front organisations. Recommended collection: financial
- [EEI 3.2 · UNCOVERED] Travel and movement indicators for suspected operatives: repeated border crossings, chartered/irregular flights, booking patterns or mobile/location data placing identified individuals in staging areas shortly before incidents. Recommended collection: border/immigration
- [EEI 3.3 · UNCOVERED] Cargo, freight or maritime movements with discrepancies (concealed/dual-use equipment, false manifests, unusual routing) detected at ports, rail hubs or via AIS that correspond to deliveries of material used in sabotage or influence operations. Recommended collection: customs/ports
- [EEI 3.4 · PARTIAL] Intercepted or otherwise-obtained communications showing tasking, coordination, or payment instructions between Russian agencies/handlers and proxy groups, including identified command-and-control servers or encrypted group identifiers. Recommended collection: signals-intel/SIGINT
Red cell review: CONCUR
TLP:CLEAR