TLP:CLEAR · Disclosure is not limited.
Europe: Russian-Linked Hybrid Threats, 10 October 2026
Time window: Last 1 day · Audience: General analyst · Type: Situation report · DTG: 2026-10-10 11:39Z · Overall confidence: MEDIUM
BLUF
European reporting points to Russian-linked activity in Estonia moving beyond symbolic targets, with the reported August attack on defence supplier Milrem and Estonia's arrest of 20 people said to have been recruited after travelling to Russia. Danish officials expect more sabotage in the coming months, while NATO has publicly attributed a broad range of hostile activity in Moldova to Russia. Public evidence independently verifying responsibility for specific incidents remains uneven.
Executive summary
Estonian Internal Security Service Director General Margo Palloson said attacks initially targeted symbolic objects, then described an August attack on Milrem, a robotics firm supplying Ukraine's military. She also said Estonia had arrested 20 people since 2025 who travelled to Russia and were then recruited by Russian intelligence. Danish officials assess that Russia is likely to increase sabotage and other attacks on Europe in the coming months. NATO Deputy Secretary General Radmila Shekerinska has attributed election interference, cyberattacks, sabotage, airspace violations, energy pressure and an unauthorised Russian troop presence in Moldova to Moscow. These statements indicate allied concern, but they do not independently verify each incident or establish a single centrally directed campaign.
Change from previous assessment
Since the 9 October brief, this update adds a more specific Estonian picture: Margo Palloson described attacks progressing from symbolic targets to Milrem and reported 20 arrests since 2025 of people recruited after travelling to Russia. It also adds NATO's detailed public allegations concerning Moldova and a Danish forecast of more attacks in the coming months. No new reporting in this update addresses the RAF Molesworth or RAF Fairford investigations, so the earlier separation of those cases remains unchanged.
Key judgments
- It is likely that Russian-linked activity in Estonia is shifting from symbolic disruption towards targeting organisations supporting Ukraine. Palloson described earlier attacks on cars, Ukrainian flags and a Ukrainian restaurant, then said Russian-directed saboteurs attacked Milrem in August. She also reported 20 arrests since 2025 of people recruited after travelling to Russia. The pattern is consistent with a move towards operational targeting, but the specific attributions rely heavily on Estonian security reporting and one major-media interview. (Confidence: medium · ASSESSED)
- I&W: Confirm: Estonian prosecutors publicly charge a suspect over the Milrem attack and identify Russian tasking or an intermediary link. (0-3 months)
- I&W: Break: The Estonian Internal Security Service or prosecutors publicly withdraw the Russian-direction attribution for the Milrem attack. (0-3 months)
- NATO's public assessment is that Russia is applying several forms of pressure against Moldova. Deputy Secretary General Radmila Shekerinska attributed election disinformation, vote buying and threats, cyberattacks and sabotage against critical infrastructure, drone and missile airspace violations, energy cut-offs and an unauthorised Russian troop presence to Moscow. This is a clear account of NATO's position, not independent verification of each allegation. (Confidence: medium · REPORTED)
- I&W: Confirm: Moldovan authorities publish forensic evidence of a drone or missile airspace violation, or a named cyber incident, and NATO repeats the Russian attribution. (0-3 months)
- I&W: Break: Moldovan officials publicly dispute Shekerinska's attribution or publish findings assigning a reported incident to another cause. (0-3 months)
- Danish officials assess that Russia is likely to increase sabotage and other attacks on Europe in the coming months. Reuters has also reported Russian targeting of defence firms in Denmark. This warning is relevant to near-term monitoring, but the supplied reporting does not provide case-level evidence or identify the Danish firms involved. (Confidence: medium · REPORTED)
- I&W: Confirm: Danish officials disclose a new sabotage case against a named Danish defence supplier and attribute it to Russian direction. (0-3 months)
- I&W: Break: Danish officials publicly revise their forecast and assess that Russian sabotage activity is stable or declining. (1-3 months)
- Russian-linked information operations targeting the UK, Ukraine and other countries are reported, but their scale and specific attribution remain insufficiently established in the available reporting. NATO has separately accused Russia of using disinformation to undermine Moldova's elections. The claims support attention to the threat, not a quantified estimate of its reach or effect. (Confidence: low · REPORTED)
- I&W: Confirm: The European External Action Service publishes case-level evidence linking a named information operation to Russian direction and identifies its target. (1-3 months)
- I&W: Break: BBC Verify or an official European source corrects or withdraws the Russian attribution for a specific operation cited in the current reporting. (1-3 months)
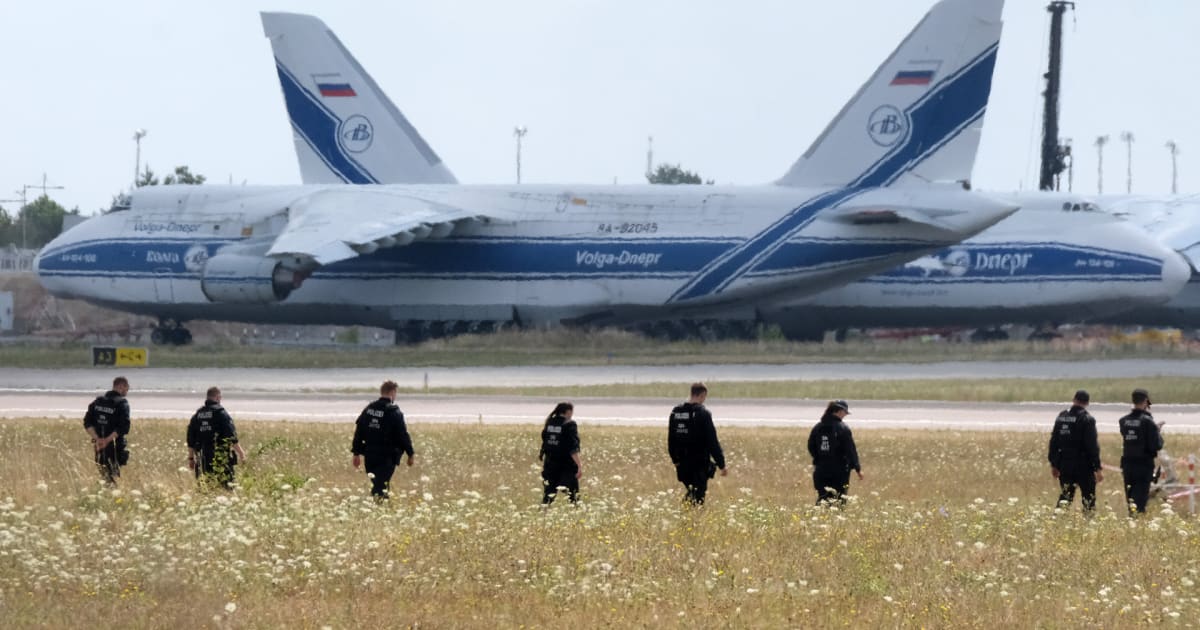
- A successful attack causing mass casualties at German aviation infrastructure is very unlikely in the near term, but remains a low-probability, high-impact warning scenario. Reporting describes an attempted explosive attack on a plane in Germany and a suspected drone attack at Leipzig/Halle Airport, both in August. The available claims do not establish an imminent plot, and the Leipzig/Halle attribution is explicitly suspected rather than confirmed. (Confidence: low · ASSESSED)
- I&W: Confirm: German authorities disclose evidence of a new plot against an aircraft or airport and attribute it to Russian intelligence. (0-3 months)
- I&W: Break: German authorities state that the Leipzig/Halle incident was not a Russian-directed attack and report no continuing aviation threat linked to the plane incident. (0-3 months)
Outlook & scenarios
Continued deniable pressure (55%)
It is likely that low-visibility sabotage, recruitment and information activity remain the main pattern. The reported Estonian cases and Danish warning point to continued pressure, while Palloson's account of intermediaries suggests that attribution will remain difficult.
Improved protection limits the impact (25%)
It is unlikely that reported attacks produce a sustained rise in damage if Estonia's physical-security advice to defence firms is adopted and other states improve protection of named suppliers and infrastructure. The available reporting establishes Estonian liaison with its defence sector, but not its results.
Attribution disputes constrain responses (15%)
It is unlikely that European governments reach consistent public attributions for every incident. Palloson said sabotage networks can involve as many as seven layers of intermediaries, which would complicate efforts to link individual perpetrators to Russia.
High-impact aviation attack (5%)
It is very unlikely that an aviation plot causes mass casualties in the near term. The reported plane attack attempt in Germany and suspected drone attack at Leipzig/Halle Airport make this a high-impact warning scenario, not evidence of an imminent operation.
Recommendations
- Track Estonian Internal Security Service and prosecutorial updates on the Milrem attack and the 20 arrests. Record separately the reported act, the suspected perpetrators and any evidence of Russian tasking.
- Treat Shekerinska's Moldova allegations as NATO's official assessment until Moldovan authorities or independently documented technical findings corroborate individual incidents. Prioritise updates on election interference, cyber incidents and reported airspace violations.
- Maintain a near-term watchlist for Danish and Estonian defence suppliers. Update assessments only when officials identify a specific incident, target and evidential basis for attribution.
- Do not use low-reliability social-media claims to quantify Russian information operations. Seek case-level evidence from the European External Action Service, BBC Verify or named national authorities before making claims about scale or impact.
- Keep the German aviation incidents on the warning list, while labelling the Leipzig/Halle attribution as suspected and the plane attack report as an attempted incident. Seek official German updates before assessing the risk as imminent.
Confidence & uncertainty
Confidence is medium because the reporting includes a primary NATO transcript and detailed major-media reporting on Estonian security claims, but the evidence for Russian responsibility in specific incidents relies heavily on official attribution and a single interview. The supplied reporting offers limited independent, case-level corroboration. Low-reliability social-media claims are not used to quantify the information threat.
Alternative analysis (red cell)
The available reporting indicates attempted or suspected activity against German aviation-related targets, but it does not establish whether these incidents represent a coherent campaign or what level of casualty risk they create. A successful mass-casualty attack may be unlikely, but the supplied evidence cannot justify the stronger estimate 'very unlikely' without a capability and intent assessment. The Leipzig/Halle attribution remains particularly uncertain because it is explicitly graded B3 (bdf18b56-3b98-4b53-9322-b3a24311b428).
Intelligence gaps
- [EEI 1.1 · PARTIAL] Reports, operator notifications, CCTV or satellite imagery showing unexplained physical damage or operational outages at critical infrastructure sites (power substations, gas pipelines/compressor stations, water treatment plants, railway signaling centers, major telecom exchanges). Recommended collection: satellite/imagery
- [EEI 1.2 · UNCOVERED] Observed reconnaissance activity around critical sites indicative of attack planning (unauthorised drone flights, repeated surveillance visits, loitering vehicles, mapping/photography of assets). Recommended collection: open-source/media
- [EEI 1.3 · UNCOVERED] Law-enforcement or customs seizures, arrests or interdictions of persons or shipments carrying explosives, sabotage tools, specialty cutting/electrical equipment, or covert comms gear destined for/near critical infrastructure. Recommended collection: law enforcement
- [EEI 2.1 · UNCOVERED] Emergence or amplification of coordinated social-media networks (sets of accounts, pages, channels) pushing identical narratives or hashtags across multiple platforms, including bot-like activity metrics and origin IP/common management indicators. Recommended collection: social-media/OSINT
- [EEI 2.2 · PARTIAL] Publication or internal guidance from state-run media, proxy outlets, or identified influence platforms distributing talking points, pre-scripted messaging, or translated content targeted at specific EU countries/communities. Recommended collection: open-source/media
- [EEI 2.3 · PARTIAL] Distribution of manipulated multimedia (deepfakes), targeted phishing/whaling campaigns, or localized false narratives timed to political events (elections, protests, court rulings) with tracked reach and engagement metrics. Recommended collection: cyber/forensic
- [EEI 3.1 · UNCOVERED] Unusual financial transactions: wire transfers, crypto conversions, or payments to shell companies, NGOs or individuals exceeding typical baselines that link to known proxies or front organisations. Recommended collection: financial
- [EEI 3.2 · PARTIAL] Travel and movement indicators for suspected operatives: repeated border crossings, chartered/irregular flights, booking patterns or mobile/location data placing identified individuals in staging areas shortly before incidents. Recommended collection: border/immigration
- [EEI 3.3 · UNCOVERED] Cargo, freight or maritime movements with discrepancies (concealed/dual-use equipment, false manifests, unusual routing) detected at ports, rail hubs or via AIS that correspond to deliveries of material used in sabotage or influence operations. Recommended collection: customs/ports
- [EEI 3.4 · UNCOVERED] Intercepted or otherwise-obtained communications showing tasking, coordination, or payment instructions between Russian agencies/handlers and proxy groups, including identified command-and-control servers or encrypted group identifiers. Recommended collection: signals-intel/SIGINT
Cited sources
[1] Foreign Policy · Russian Sabotage in Europe Is No Longer ‘Symbolic’ (A) · 9 October 2026 · sha256:4166d2c98ade [2] NATO (North Atlantic Treaty Organization) · Speech by NATO Deputy Secretary General Radmila Shekerinska at the Moldova Security Forum 2026 (A) · sha256:a2de8b184391 [3] BBC News (BBC Verify) · BBC Verify | Latest News & Updates | BBC News (A) · sha256:b2bb51602691 [4] Council on Foreign Relations (CFR) · Russia’s Attacks in Europe Are Escalating. Here Is How to Push Back. (B) · 9 October 2026 · sha256:6905a2a41fba
Source content hashes were computed at collection time; the cited text is preserved unmodified for the life of this product.
Red cell review: PARTIAL DISSENT
TLP:CLEAR