TLP:CLEAR · Disclosure is not limited.
European Hybrid Threats: Attribution Remains Unresolved
Time window: Last 1 day · Audience: General analyst · Type: Situation report · DTG: 2026-11-07 12:44Z · Overall confidence: HIGH
BLUF
Bomb threats continued to disrupt European flights and newsrooms, but the available reporting does not establish Russian state direction. Separate cyber incidents affected Italian Foreign Minister Antonio Tajani's personal data and the Brenner Base Tunnel company, while the reported impact on operations at the tunnel company was limited.
Executive summary
Threats reported from 3 to 6 November targeted flights in several European countries and media organisations in Ireland and Bulgaria. Prague's airport reported nine threatened flights on 6 November, and France reported four targeted flights; counts across reports vary, and no explosives were found on affected aircraft. European security agencies are investigating a possible Russian trace, but Male State denied involvement and the Irish government said responsibility was unknown. On 7 November, reporting also described publication of Tajani's and his family's personal data, which Giorgia Meloni characterised as linked to pro-Russian hackers, and unauthorised access to some data at BBT SE, the company building the Brenner Base Tunnel. BBT SE said operations were unaffected. A separate report of Russian media amplification of Ukrainian allegations rests on one blog and does not establish a coordinated disinformation campaign.
Change from previous assessment
Since the 6 November brief, the threat pattern remains active in reporting, and European security agencies are now reported to be investigating a possible Russian trace. The public evidence still does not establish Russian state direction, so confidence in attribution remains low. This brief adds judgments on the Tajani data exposure, the BBT SE intrusion, Germany's reported sabotage threat assessment and the thin reporting on disinformation. It does not raise confidence in cross-target coordination.
Key judgments
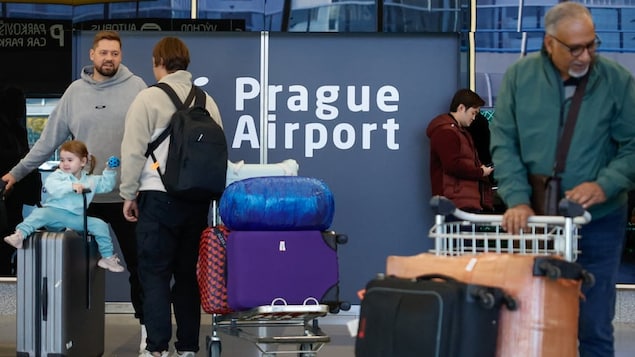
- The bomb-threat campaign almost certainly caused repeated operational disruption across Europe from 3 to 6 November. Prague's Vaclav Havel Airport reported nine threatened flights on 6 November, France reported four targeted flights, a Wizz Air flight from Prague to Rome diverted to Venice, and bomb threats prompted evacuations at RTÉ and other Dublin media offices. No explosives were reported on affected aircraft. Flight totals vary across reports, so a single cumulative figure is not established. (Confidence: high · REPORTED)
- I&W: Prague Airport and French authorities publish reconciled incident records confirming the reported nine Prague flights and four French flights; this would strengthen the reported scale. Corrections showing duplicate or misclassified incidents would weaken it. (0-14 days)
- I&W: Police or affected operators confirm that the Dublin newsroom evacuations and the Wizz Air diversion followed separate threats; evidence that these reports refer to a single incident would weaken the assessment of repeated disruption. (0-14 days)
- It is unlikely that public evidence available on 7 November establishes Russian state direction or Male State responsibility for the flight and newsroom threats. European security agencies are investigating a possible Russian trace, but the Irish government said responsibility was unknown, Male State and its founder denied involvement, and the attribution to Male Legion appears in a blog report. The competing claims leave attribution unresolved. (Confidence: low · ASSESSED)
- I&W: A named European law-enforcement agency publishes forensic findings linking the threat messages or sender infrastructure to Russian state or proxy actors; this would strengthen attribution. (0-14 days)
- I&W: Investigators identify a sender with no Russian state or proxy connection, or formally rule out such a link; this would weaken attribution to Russia. (0-14 days)
- It is likely that cyber criminals published personal data belonging to Italian Foreign Minister Antonio Tajani and his family on the dark web. Prime Minister Giorgia Meloni described the activity as involving pro-Russian hackers, and Tajani said his position on Ukraine was the political reason he had been targeted. The available reporting contains no technical evidence establishing Russian state direction, and the attribution rests on one major-media account quoting the officials. (Confidence: medium · ASSESSED)
- I&W: Italian police or the Foreign Ministry publish forensic findings identifying the source of the data and linking it to a pro-Russian network; this would strengthen the reported attribution. (0-14 days)
- I&W: An official forensic update identifies a different source or finds no evidence linking the intrusion to pro-Russian actors; this would weaken the attribution. (1-3 months)
- The 7 November intrusion at BBT SE likely exposed some internet-accessible data, but the company said its operational activities were unaffected. The incident and impact are reported in one local-media account quoting BBT SE, so confidence is medium; the available reporting does not attribute the intrusion to Russia. (Confidence: medium · REPORTED)
- I&W: BBT SE releases a forensic update specifying which data or systems were accessed and whether railway construction or operational functions were affected; this would confirm or revise the reported impact. (0-14 days)
- I&W: An independent technical assessment finds that operational systems at BBT SE were affected; this would break the assessment that the impact was limited to data access. (1-3 months)
- The German military's reported assessment indicates broader official concern about Russian sabotage, extending beyond military training sites and major installations. Germany had raised its threat assessment to substantial after a drone carrying a canister of explosives was found near another airbase, and had accused Russia of a failed explosive-drone attack at Leipzig/Halle Airport. These reports do not independently establish Russian responsibility for additional incidents. (Confidence: medium · ASSESSED)
- I&W: The German military publishes an updated assessment or identifies a further case involving a civilian or transport site outside military installations; this would confirm the reported broadening of concern. (1-3 months)
- I&W: German authorities revise the substantial threat level or clarify that the cited incidents do not indicate a broader threat beyond military sites; this would weaken the assessment. (1-3 months)
- It is unlikely that the available reporting establishes a coordinated Russian disinformation campaign during this reporting period. One GDELT blog alleges that Russian media amplified Ukraine's NABU Operation Carthage corruption probe and allegations of a secret torture prison near Kyiv, but the supplied reporting provides no independent corroboration or evidence of coordination. (Confidence: low · ASSESSED)
- I&W: Independent monitoring publishes dated examples from identifiable Russian media outlets repeating the Operation Carthage or secret-prison allegations; this would strengthen the reported claim of amplification. (1-3 months)
- I&W: Archives of the outlets identified by independent monitoring show no repeated coverage of those allegations; this would weaken the claim of coordinated amplification. (1-3 months)
Outlook & scenarios
Threats continue without confirmed Russian attribution (55%)
A further wave of hoax threats is likely to prompt precautionary responses at European airports or media organisations. Investigators continue to examine sender identity, while flight totals and any link among targets remain unresolved.
Investigation identifies a Russian-linked proxy (25%)
There is an unlikely prospect that European investigators publish evidence connecting the threat messages to a Russian-linked proxy. Such findings would change the attribution assessment, but would not by themselves establish Russian state tasking.
Separate criminal or copycat activity (15%)
There is an unlikely prospect that investigators identify unrelated individuals or copycats behind the threats and cyber incidents. In this scenario, the incidents remain disruptive but do not form a centrally directed Russian operation.
A hoax coincides with operational damage (5%)
A very unlikely, high-impact scenario is that a future threat coincides with an actual intrusion or physical incident that disrupts transport operations. Current reporting does not show operational disruption at BBT SE or explosives on the threatened aircraft.
Recommendations
- Maintain a shared incident log for European flight and newsroom threats. Record the date, target, threat channel, operational response, source and investigation status, and keep separate counts for threats, affected flights and alerts until authorities reconcile them.
- Track public updates from European security agencies and national police on sender identity and forensic attribution. Distinguish evidence of a Russian-linked actor from evidence of Russian state direction.
- Request a follow-up on the Tajani data exposure that separates the confirmed publication of personal data from the still-unverified attribution. Record any technical findings released by Italian police or the Foreign Ministry.
- Seek a technical update from BBT SE on the data and systems accessed, and whether any railway-related operations were affected. Do not infer Russian involvement from the incident alone.
- Treat the Operation Carthage amplification report as an uncorroborated lead. Require dated examples from identifiable outlets and independent monitoring before assessing it as a coordinated Russian disinformation effort.
Confidence & uncertainty
Overall confidence is high for the occurrence and operational effects of the flight and newsroom threats, supported by reporting from major media, Prague Airport, Ryanair, French authorities and affected broadcasters. The principal uncertainties are attribution and scope: reported flight totals differ, Male State denied involvement, and public reporting does not establish Russian state direction. Confidence is lower for the Tajani attribution, the single-account BBT SE reporting and the blog-only disinformation allegation.
Intelligence gaps
- [EEI 1.2 · UNCOVERED] Observed reconnaissance activity around critical sites indicative of attack planning (unauthorised drone flights, repeated surveillance visits, loitering vehicles, mapping/photography of assets). Recommended collection: open-source/media
- [EEI 1.3 · UNCOVERED] Law-enforcement or customs seizures, arrests or interdictions of persons or shipments carrying explosives, sabotage tools, specialty cutting/electrical equipment, or covert comms gear destined for/near critical infrastructure. Recommended collection: law enforcement
- [EEI 2.1 · UNCOVERED] Emergence or amplification of coordinated social-media networks (sets of accounts, pages, channels) pushing identical narratives or hashtags across multiple platforms, including bot-like activity metrics and origin IP/common management indicators. Recommended collection: social-media/OSINT
- [EEI 2.2 · PARTIAL] Publication or internal guidance from state-run media, proxy outlets, or identified influence platforms distributing talking points, pre-scripted messaging, or translated content targeted at specific EU countries/communities. Recommended collection: open-source/media
- [EEI 2.3 · PARTIAL] Distribution of manipulated multimedia (deepfakes), targeted phishing/whaling campaigns, or localized false narratives timed to political events (elections, protests, court rulings) with tracked reach and engagement metrics. Recommended collection: cyber/forensic
- [EEI 3.1 · UNCOVERED] Unusual financial transactions: wire transfers, crypto conversions, or payments to shell companies, NGOs or individuals exceeding typical baselines that link to known proxies or front organisations. Recommended collection: financial
- [EEI 3.2 · UNCOVERED] Travel and movement indicators for suspected operatives: repeated border crossings, chartered/irregular flights, booking patterns or mobile/location data placing identified individuals in staging areas shortly before incidents. Recommended collection: border/immigration
- [EEI 3.3 · PARTIAL] Cargo, freight or maritime movements with discrepancies (concealed/dual-use equipment, false manifests, unusual routing) detected at ports, rail hubs or via AIS that correspond to deliveries of material used in sabotage or influence operations. Recommended collection: customs/ports
- [EEI 3.4 · UNCOVERED] Intercepted or otherwise-obtained communications showing tasking, coordination, or payment instructions between Russian agencies/handlers and proxy groups, including identified command-and-control servers or encrypted group identifiers. Recommended collection: signals-intel/SIGINT
Red cell review: CONCUR
TLP:CLEAR